Compliance, continuously.
grComply is the GRC operating system for organisations that must prove control, evidence, risk, and audit readiness across frameworks — without losing tenant branding, deployment flexibility, or auditor trust. A GRC platform is software that governs compliance controls, tracks risk, and manages audit evidence in one system instead of scattered spreadsheets. grComply does this across multiple frameworks at once — ISO 27001, SOC 2, NIST, CIS, DORA and regional regulations — sharing one control tree with cross-framework mapping, and adds policies, obligations, DPIAs, security posture management and security awareness training to the same record. It comes in five plans, from cloud to air-gapped private on-prem.
One inventory, every framework
Multi-framework, one inventory
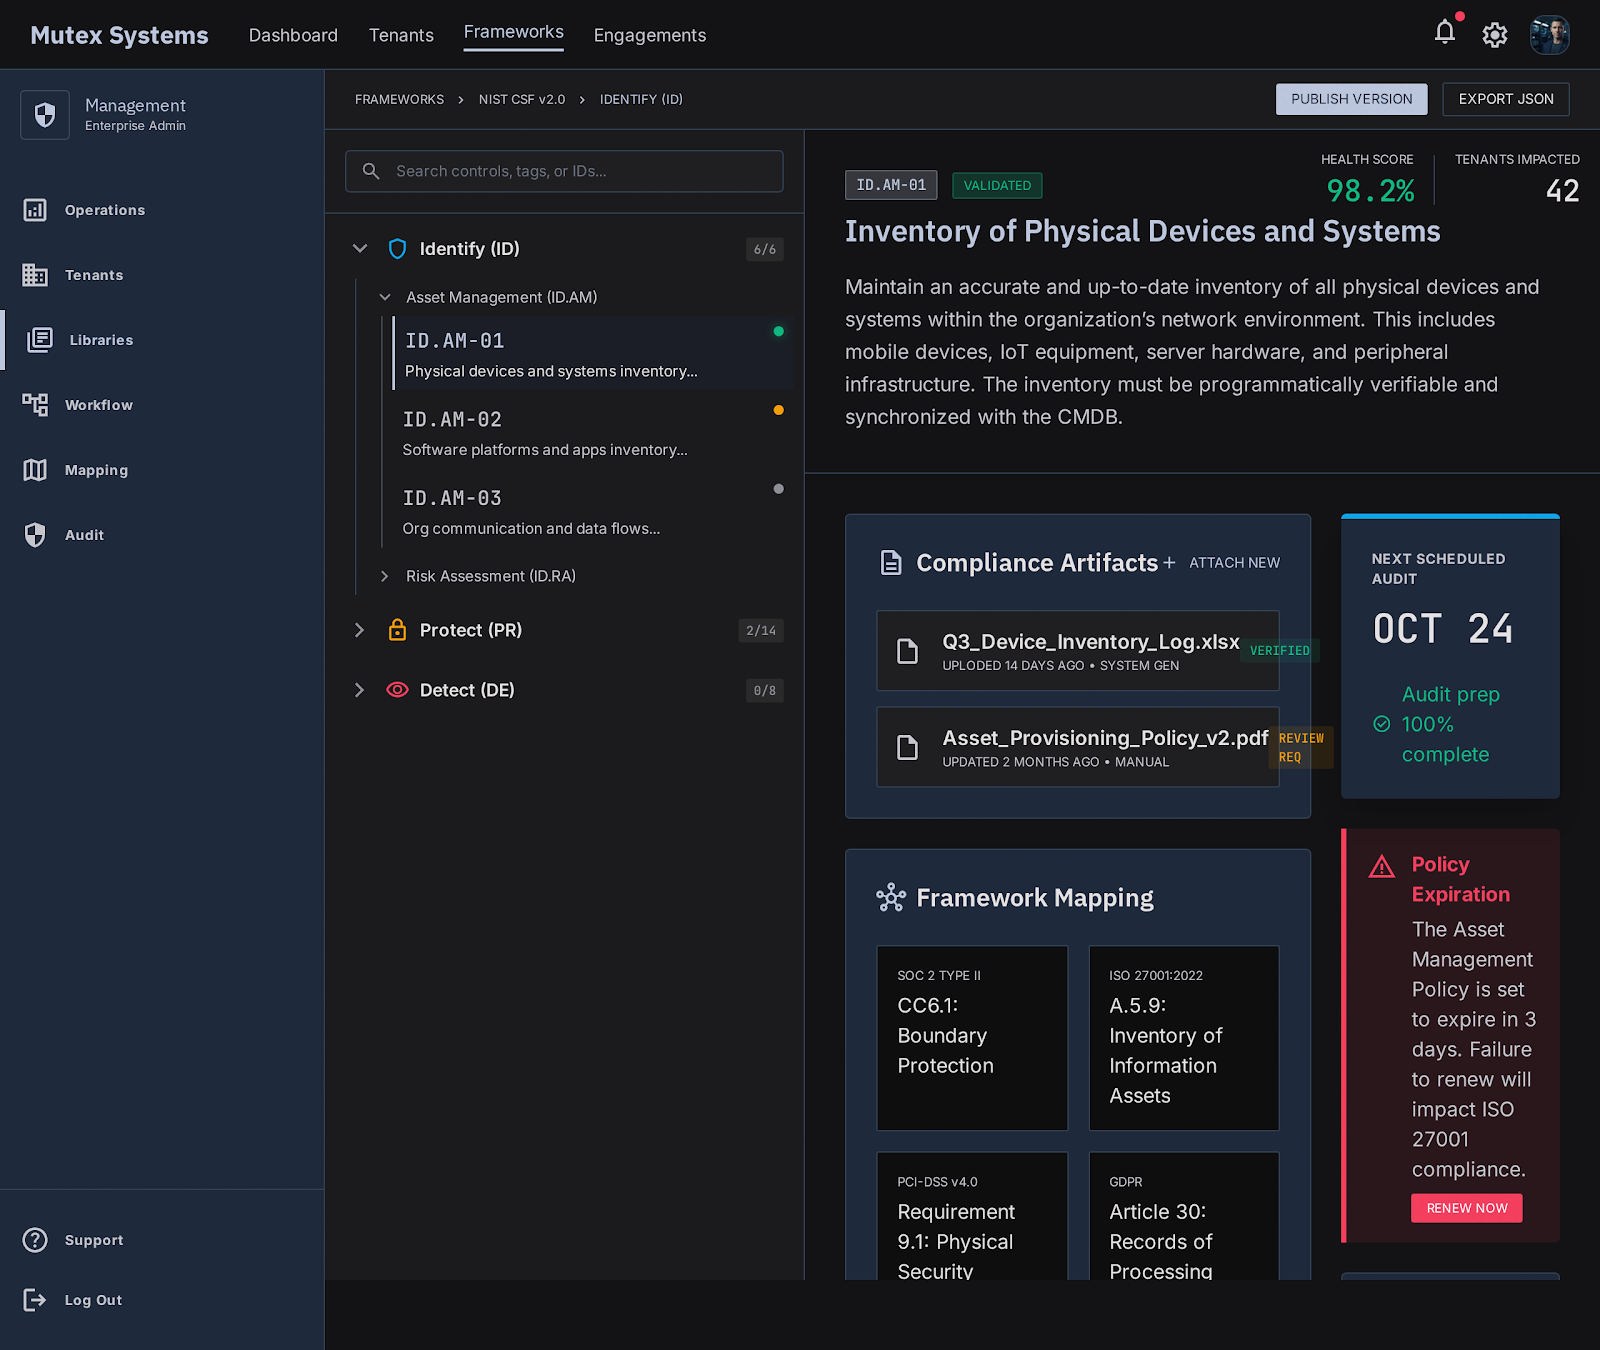
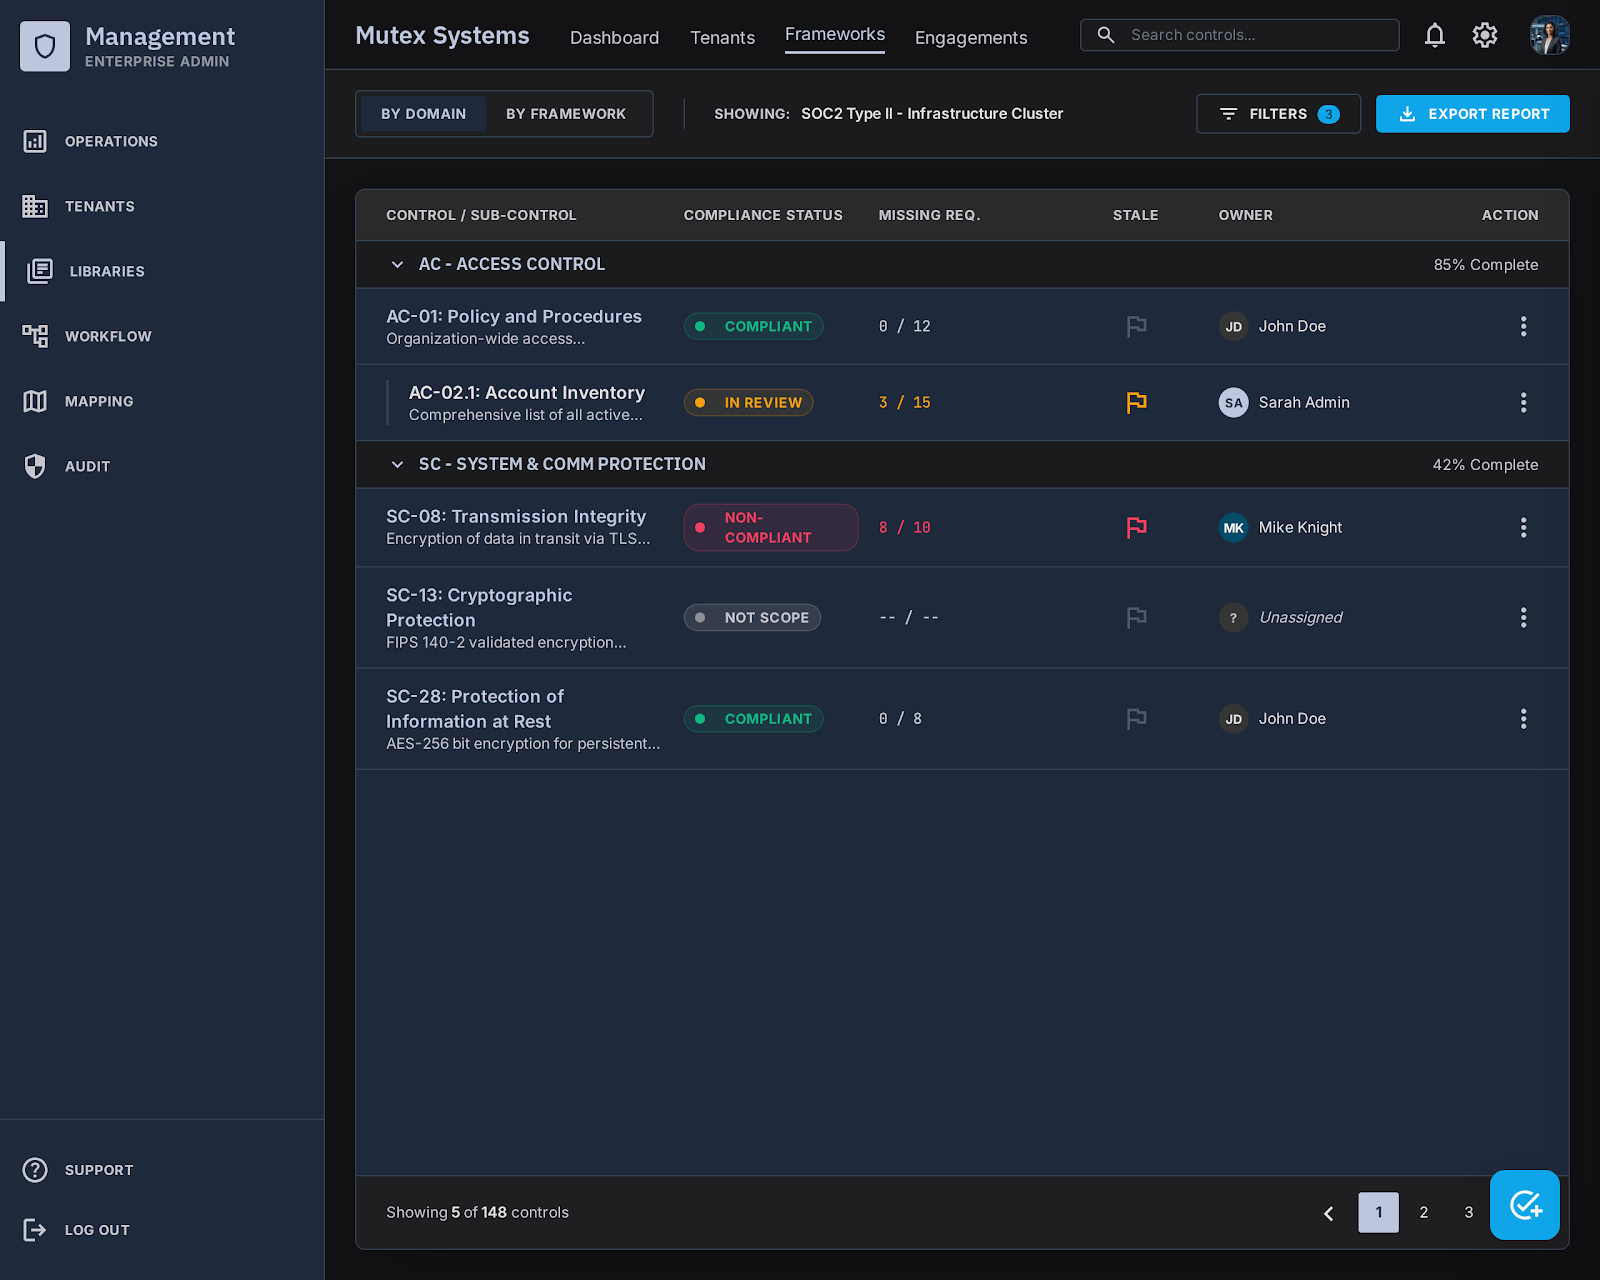
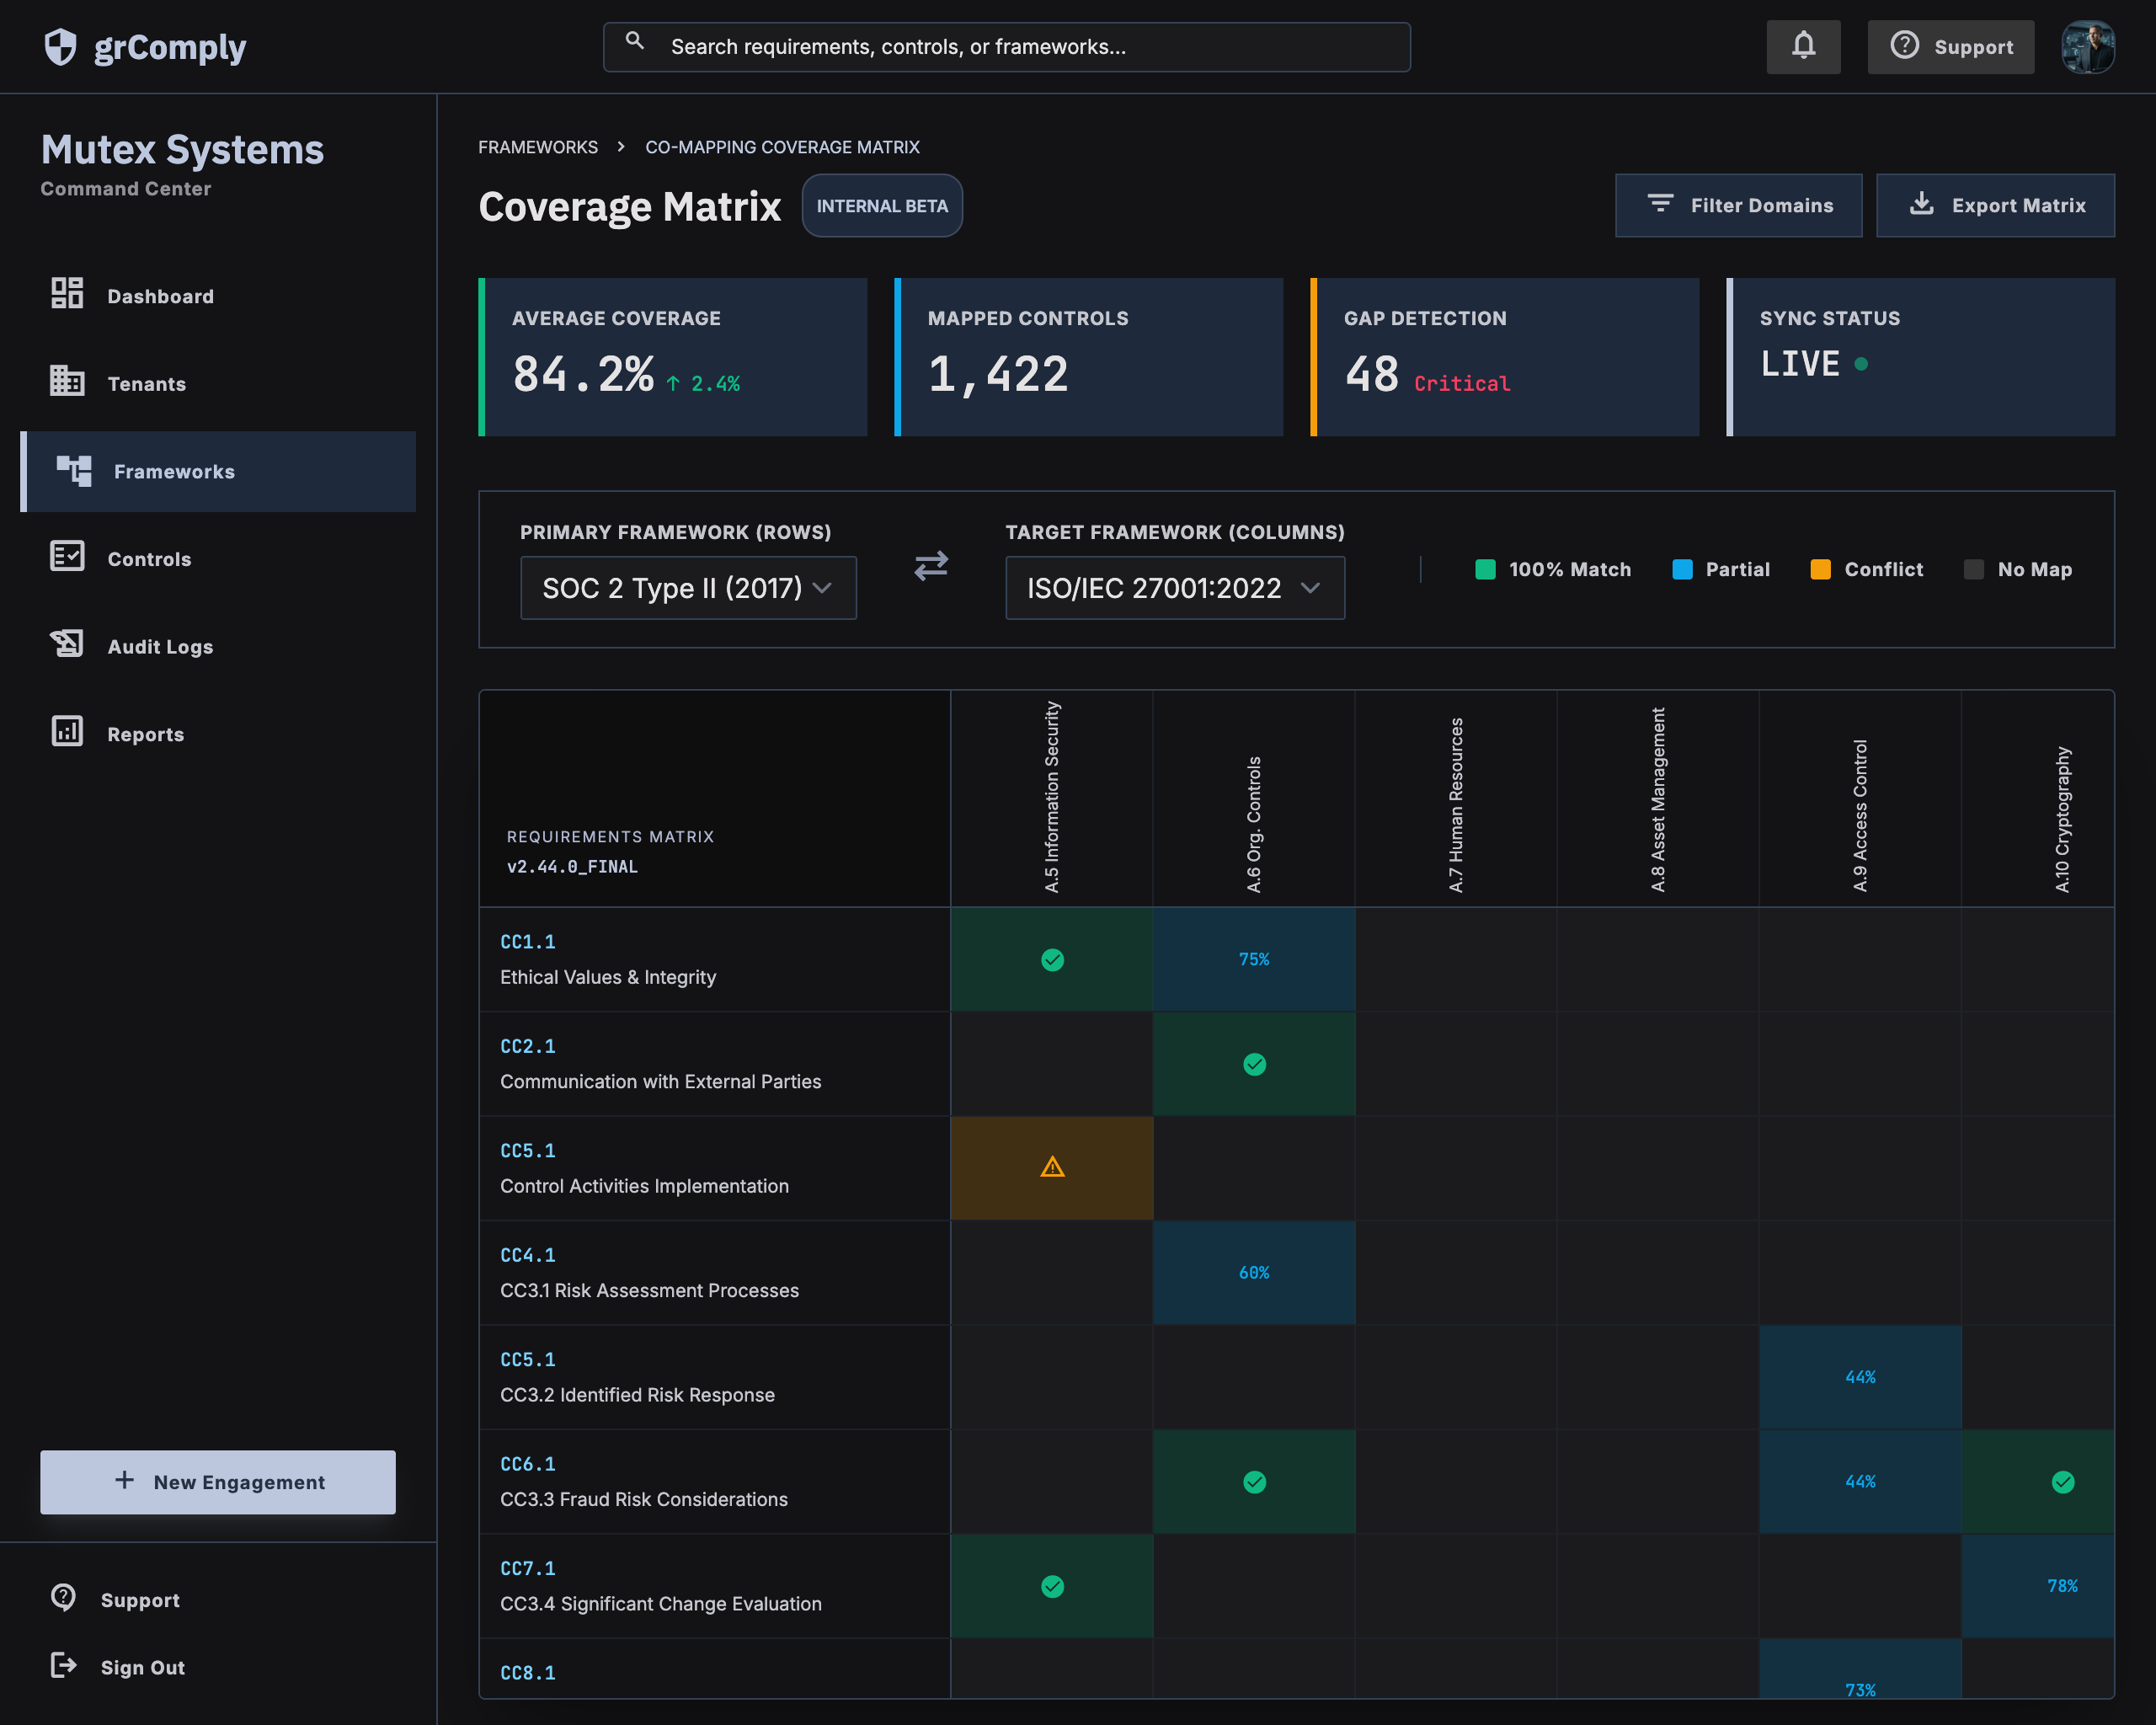
Map once, cover many. NIST, CIS, SOC 2, and tenant frameworks share one control tree with cross-framework mapping, coverage matrices, and an impact preview before you adopt a new framework version.
Client brand first
Tenant logos and names own the workspace and every export package. grComply stays quiet infrastructure — the way auditors and executives expect a compliance tool to behave.
Cloud to air-gap
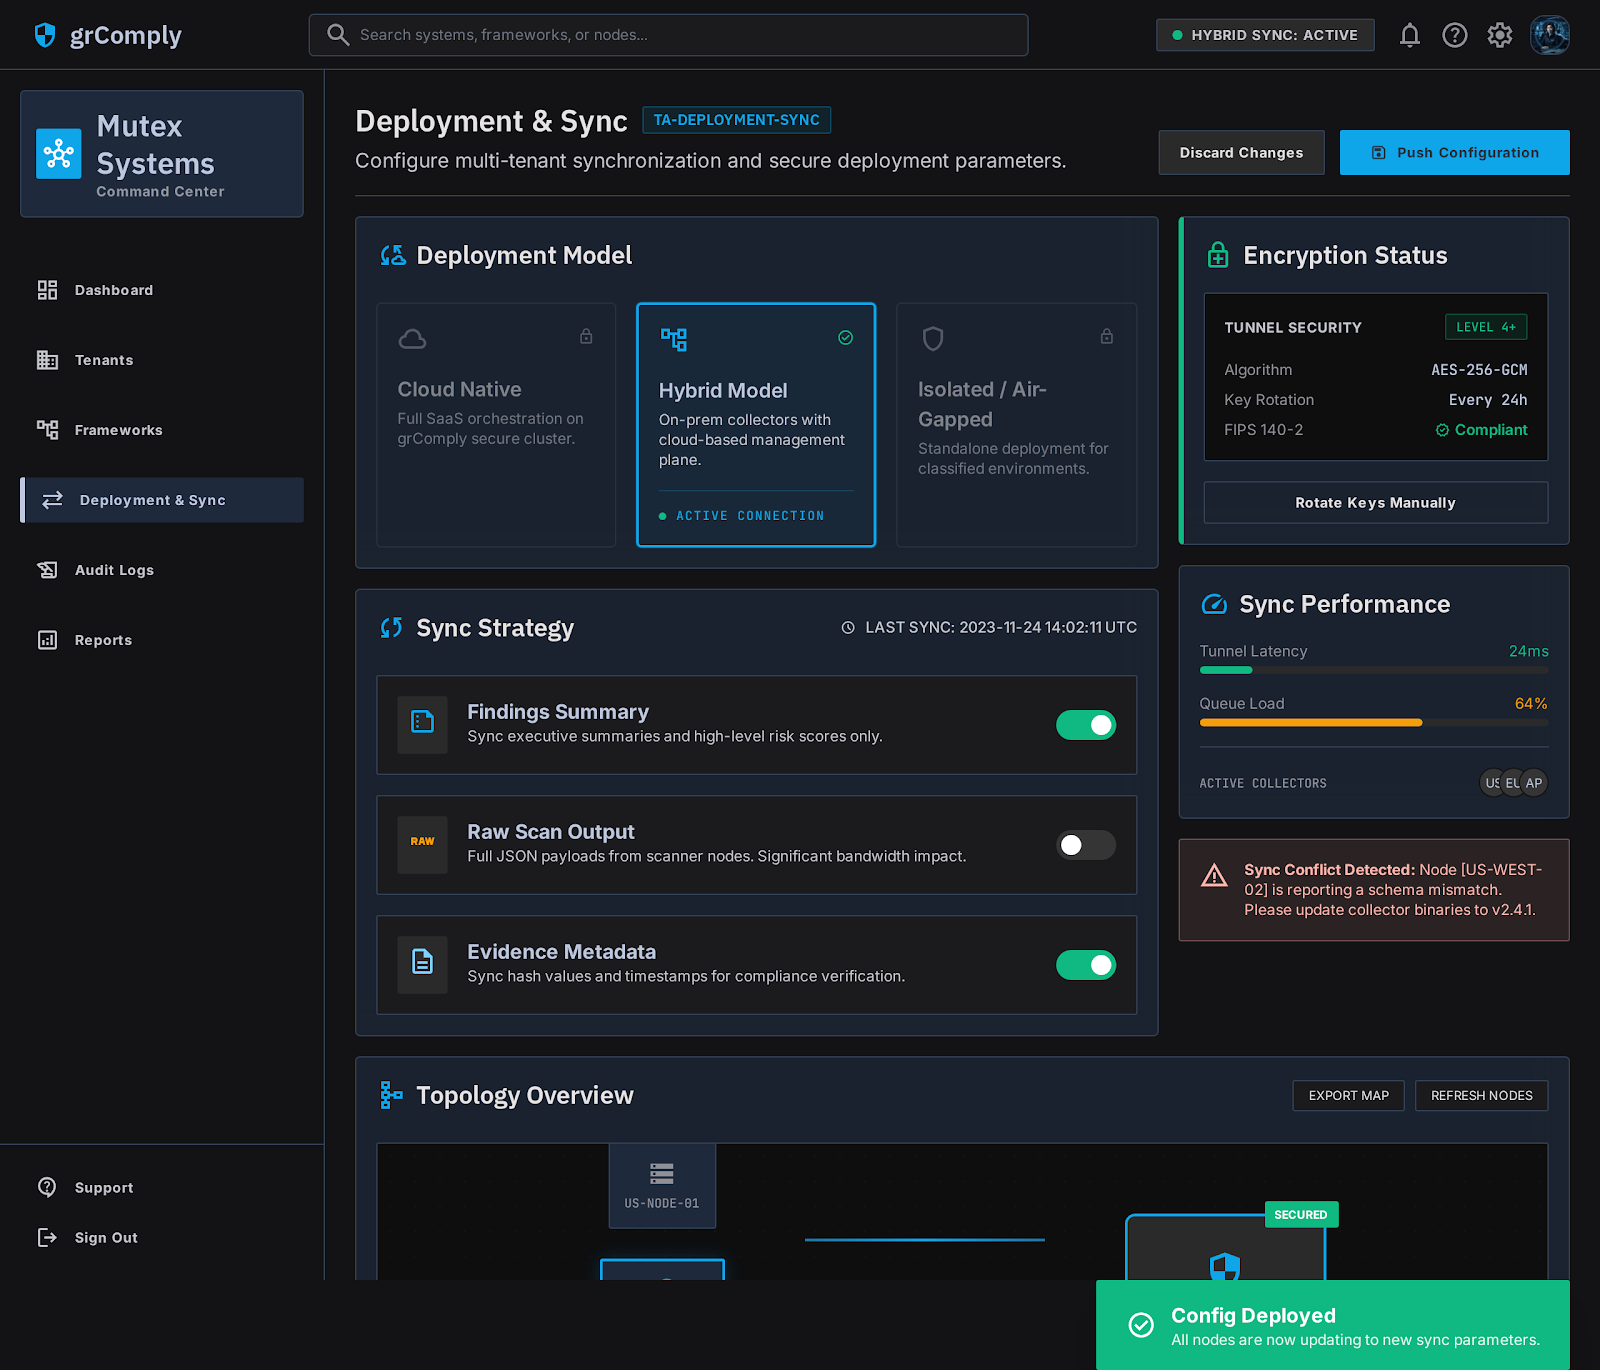
Same product, three postures: cloud for speed, hybrid sync for regulated estates, and private on-prem for air-gapped programmes — chosen by plan, with licence activation that never needs inbound access.
Discover, triage, risk
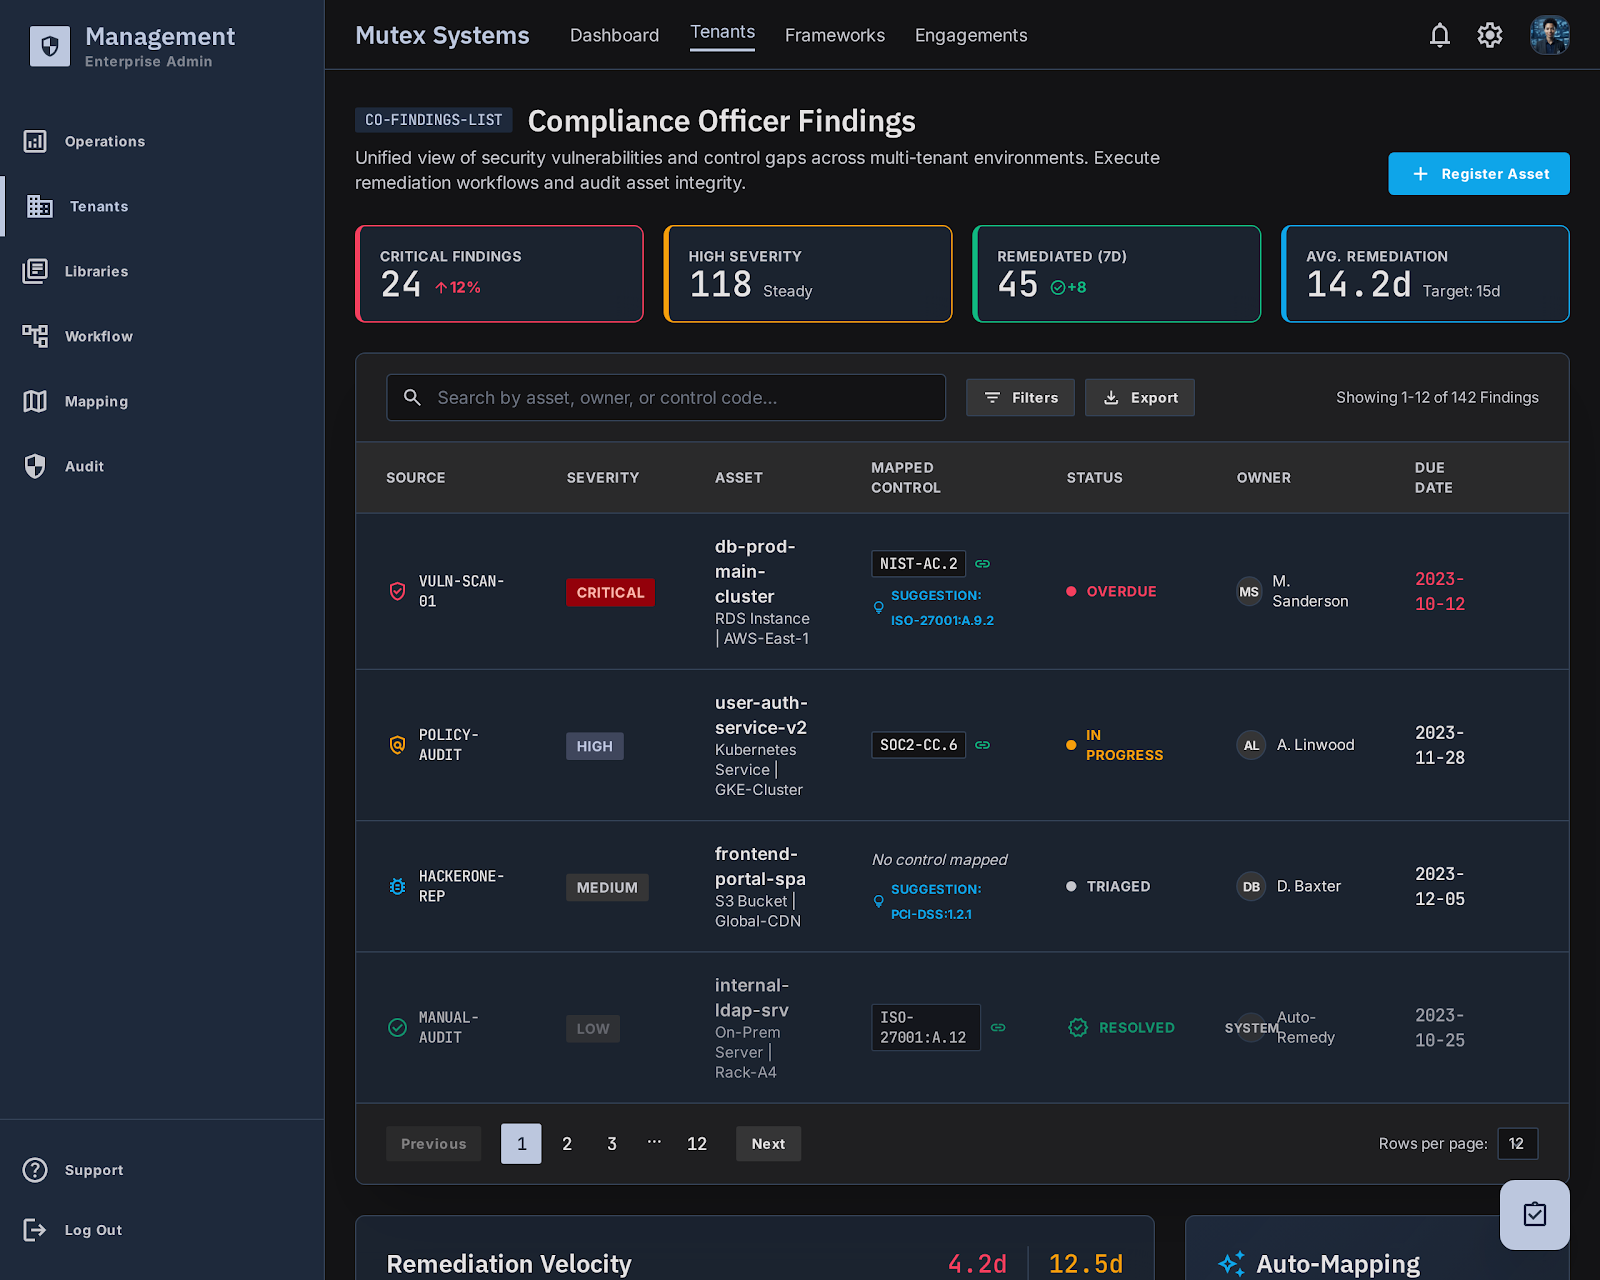
Security posture management brings external and internal scanning, device checks and configuration baselines into one view; findings link to assets with named owners, map to controls, and become risks in a register scored your way.
Auditor-grade delivery
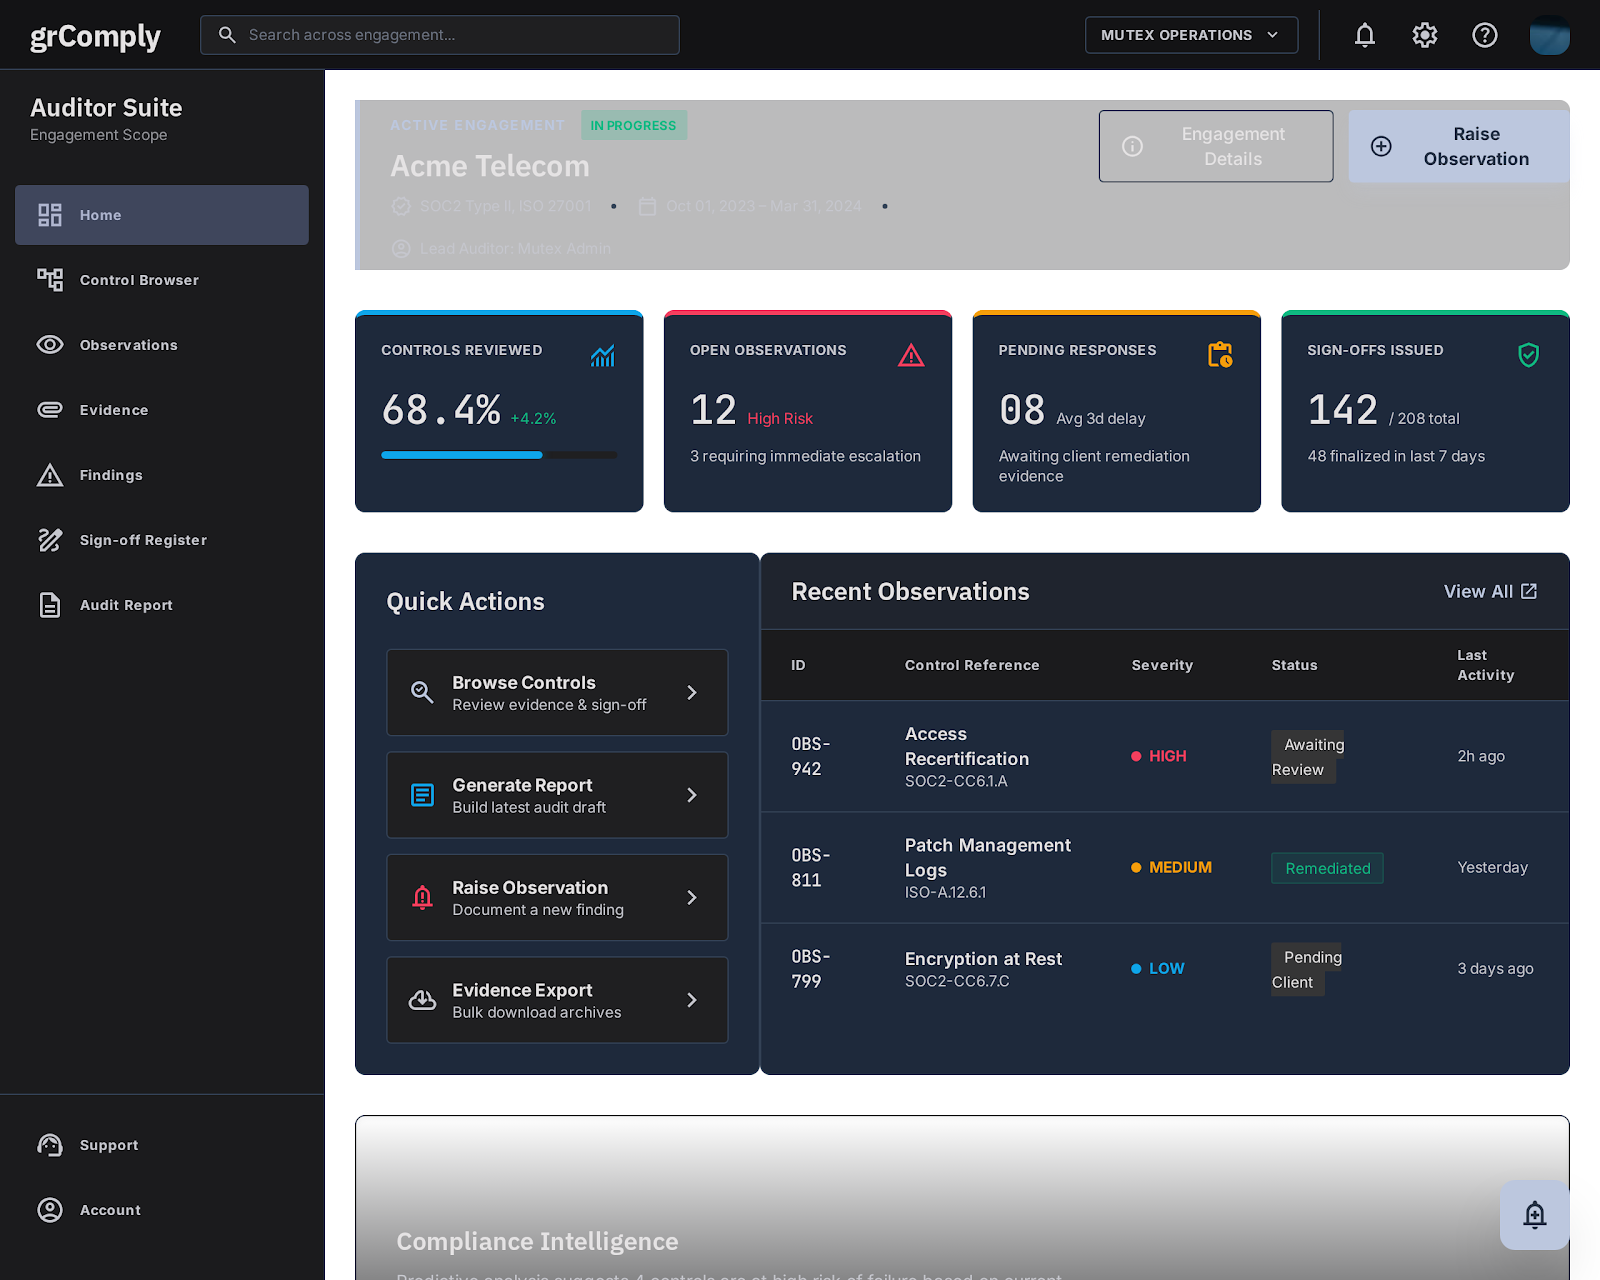
Observations, responses, peer countersign, control sign-offs, and versioned audit reports — built for how audit engagements actually run, not how a slide deck describes them.
AI that stays accountable
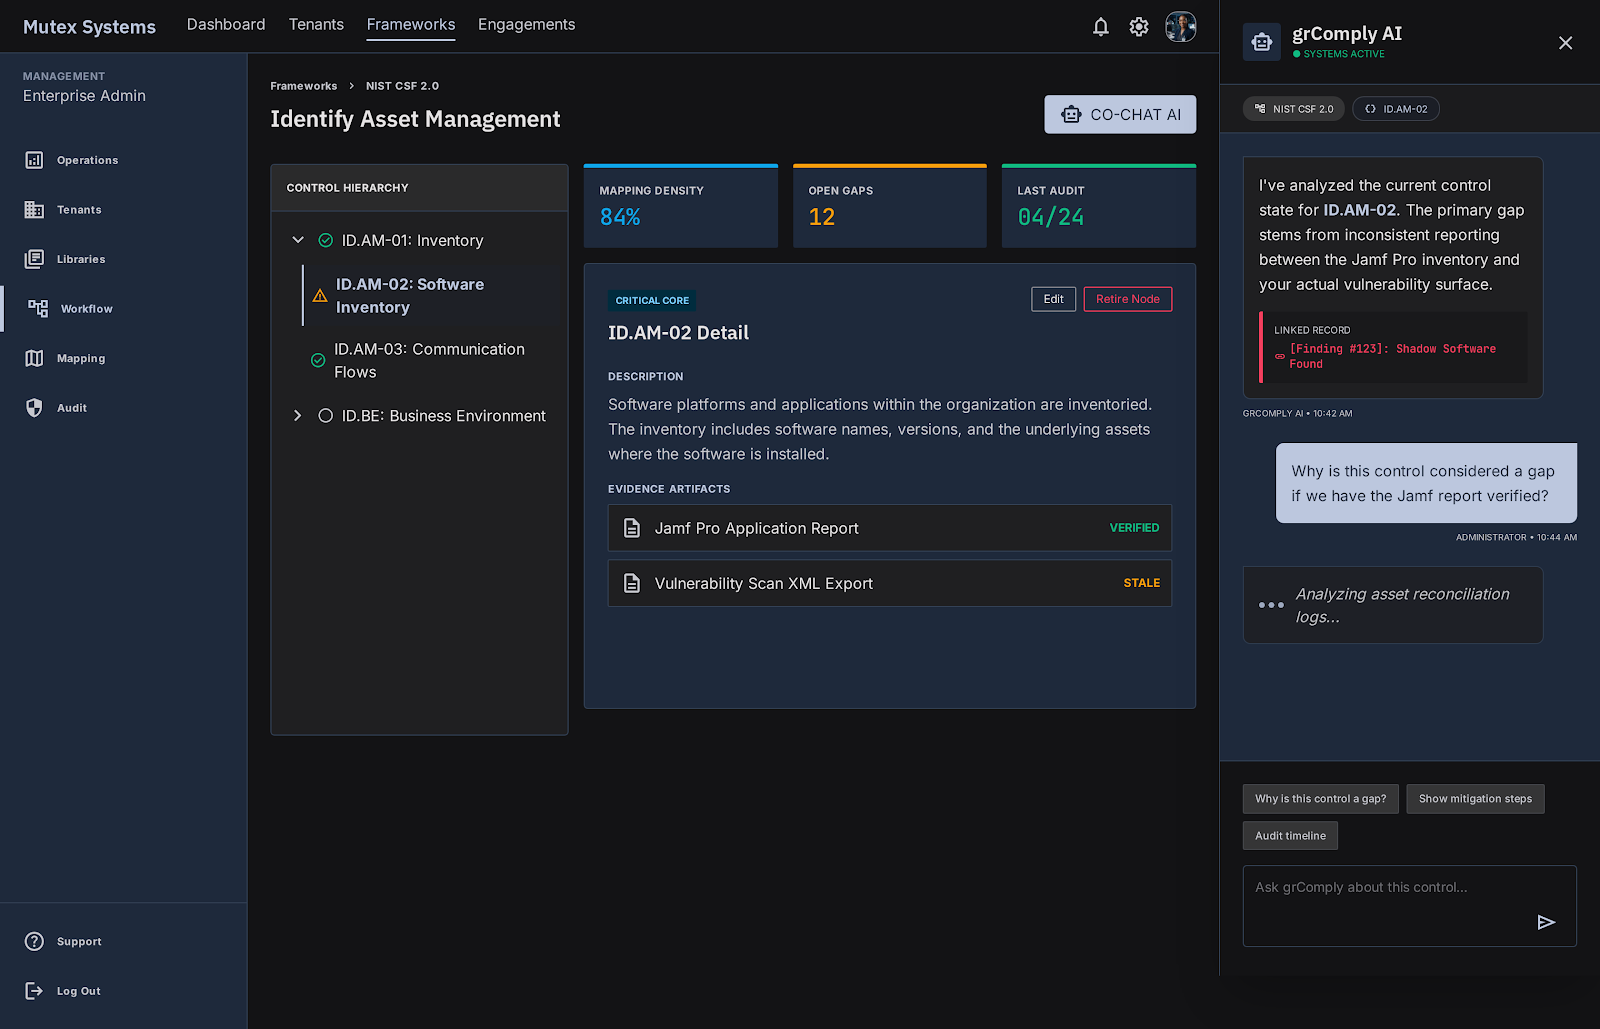
The AI assistant and policy search answer from your own workspace and cite their sources. Drafts stay drafts until a person confirms — grComply never treats machine-generated text as verified evidence.
Every module, built for how compliance actually runs
Control mapping and coverage
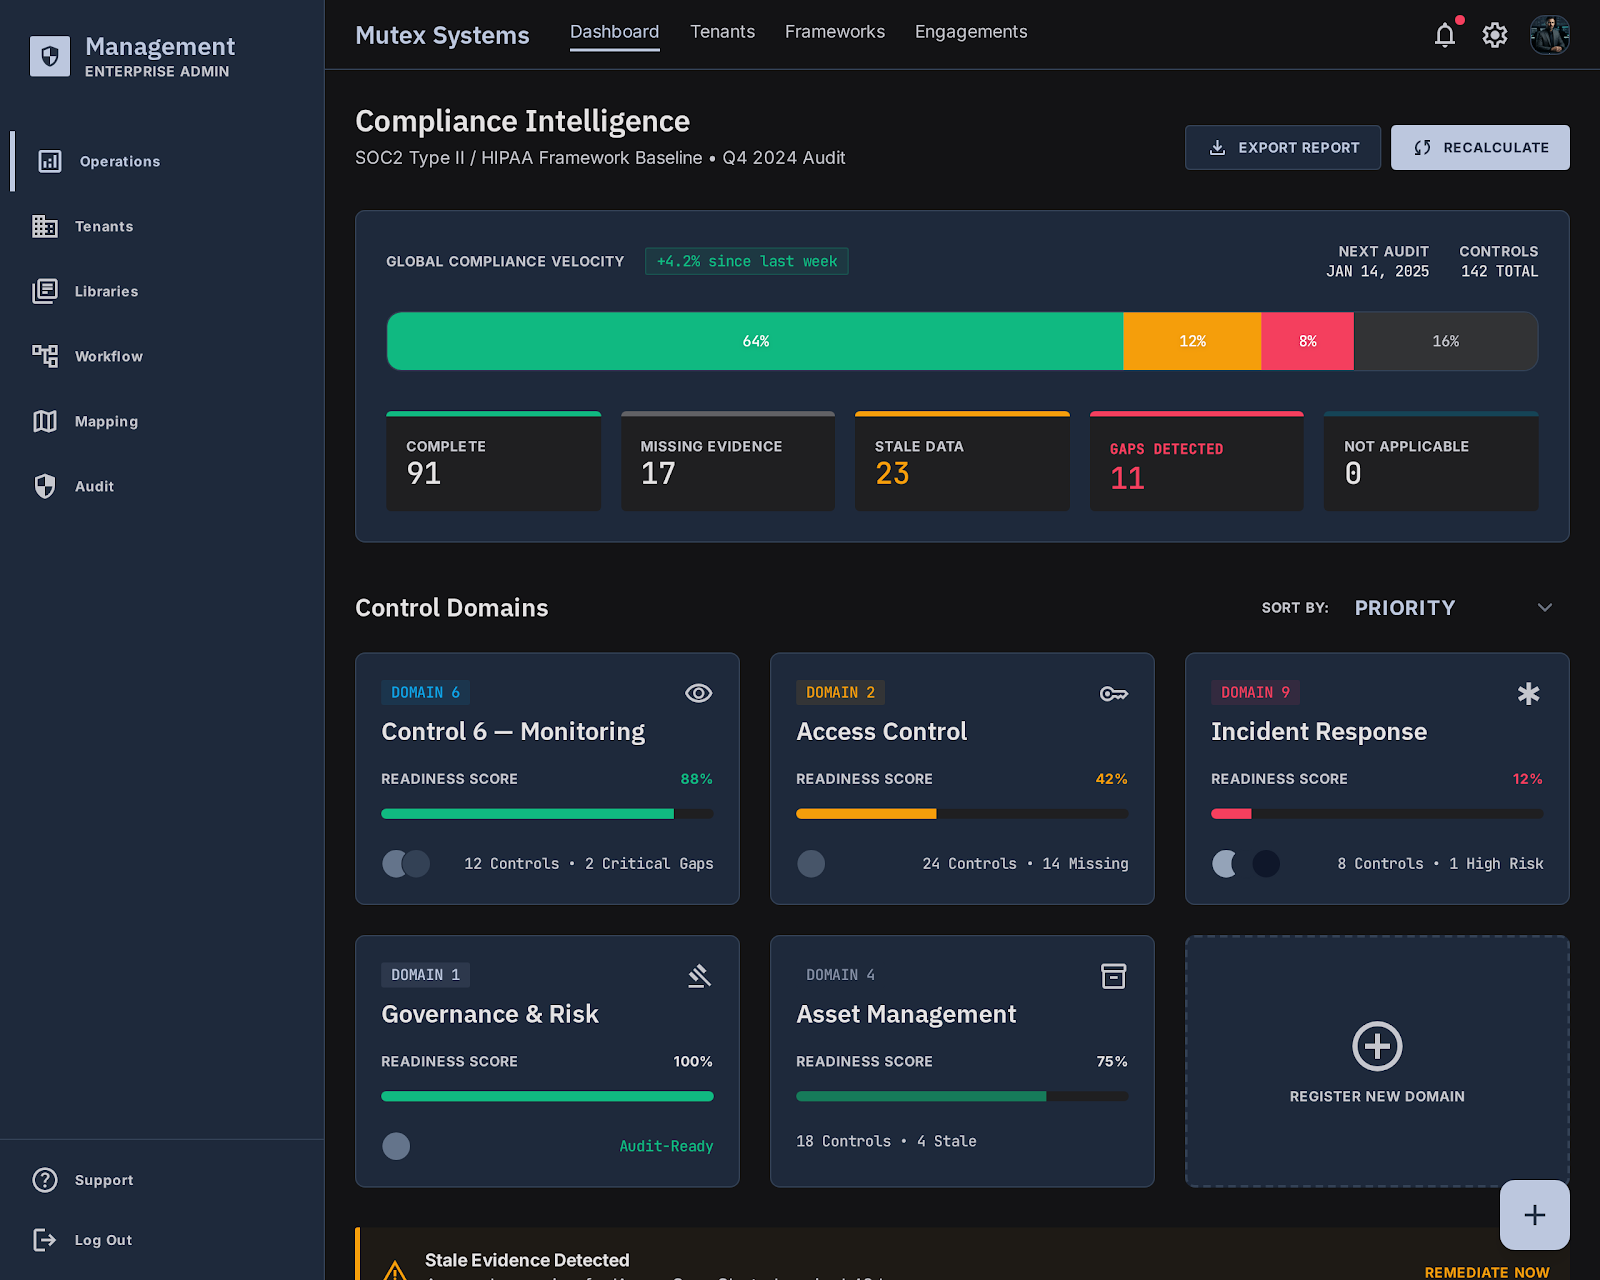
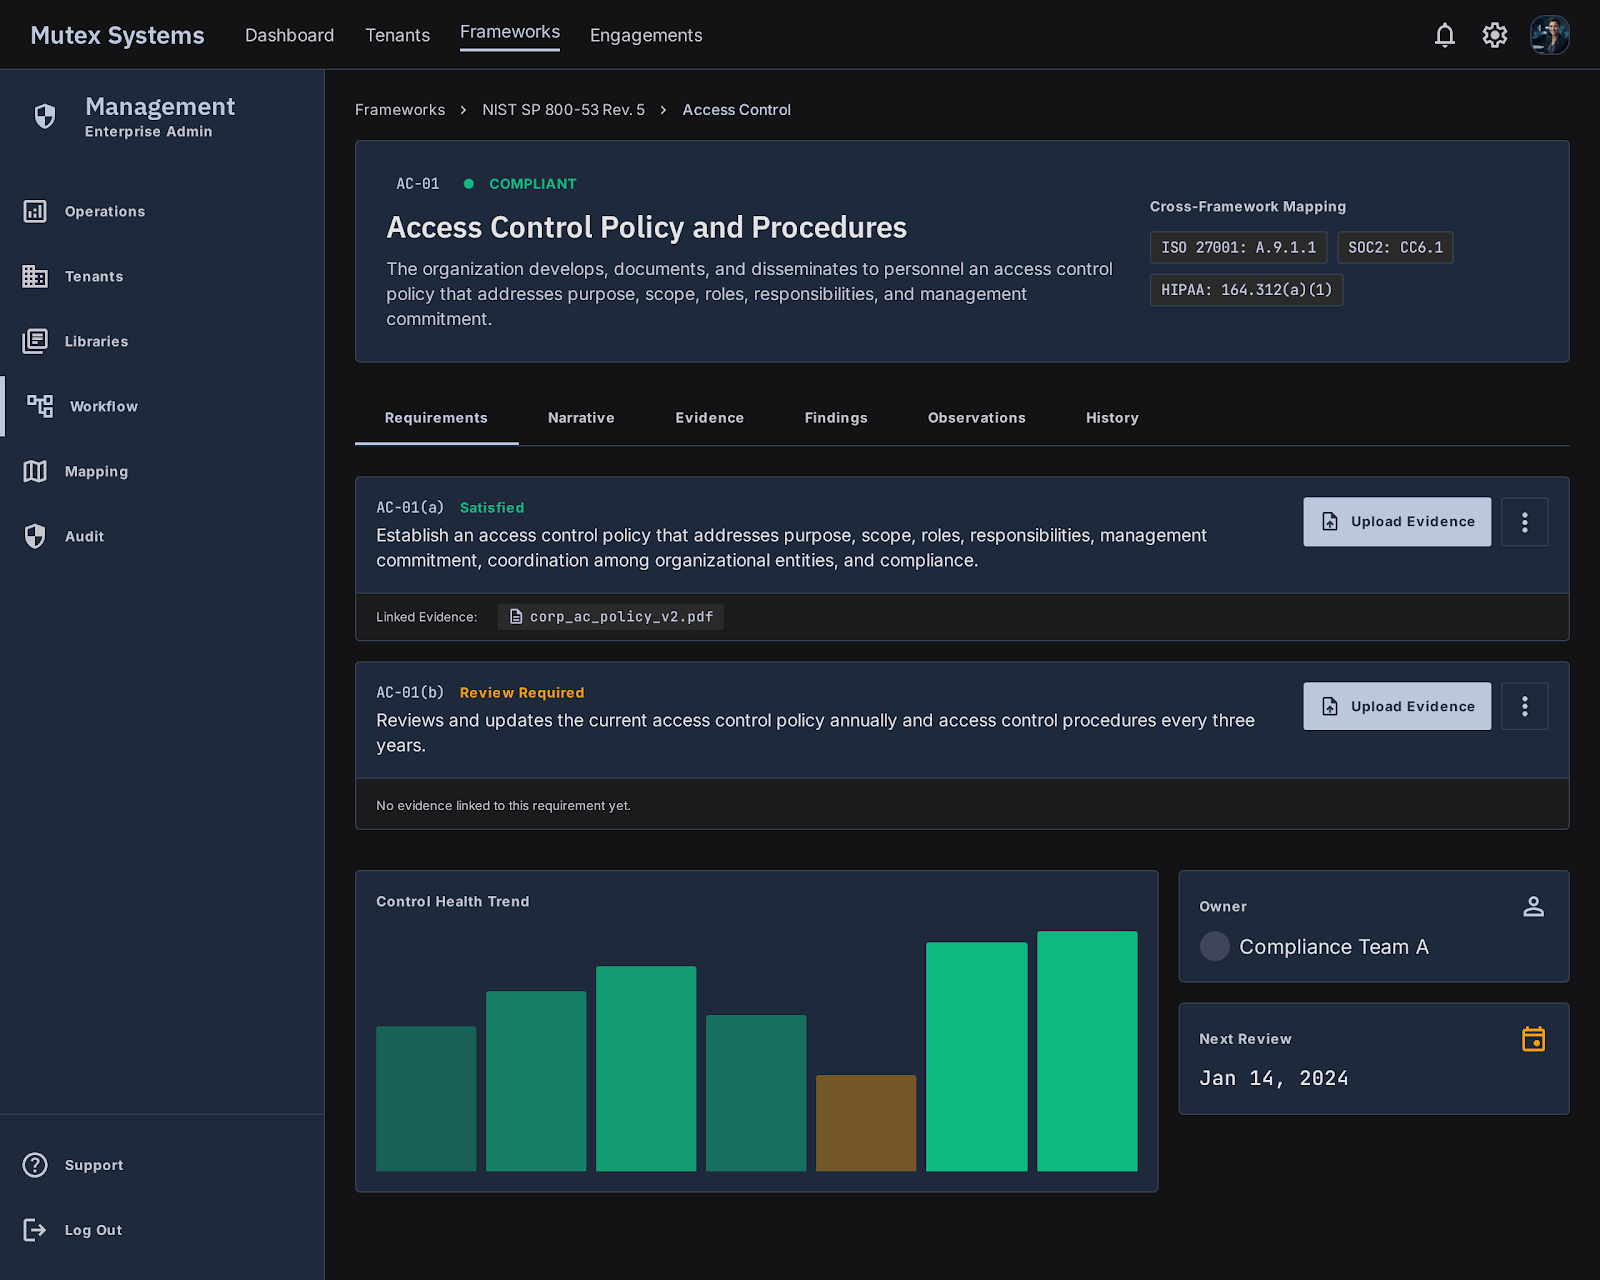
grComply's control browser gives compliance officers a technical, dense view of the framework tree rather than a simplified dashboard. Declare a control not-applicable, publish narratives, and track completion — with a cross-framework coverage matrix showing what one control covers across every adopted framework, and an impact preview before you take on a new framework version. Status vocabulary is auditor-recognised: Compliant, Partial, Gap, N/A — one language across controls, dashboards, and exports. 13 frameworks are seeded today — international standards and regional regulations alike — and any additional framework loads as data, not code.
See every supported framework →Evidence management
Evidence attaches directly to requirements — upload, approve, version, and store. The completion cache updates live, so executives see current readiness rather than last month's export. Every artefact is versioned, every approval sits on a defined path before it credits toward completion, and every export is built to survive scrutiny.
Vulnerability management and findings
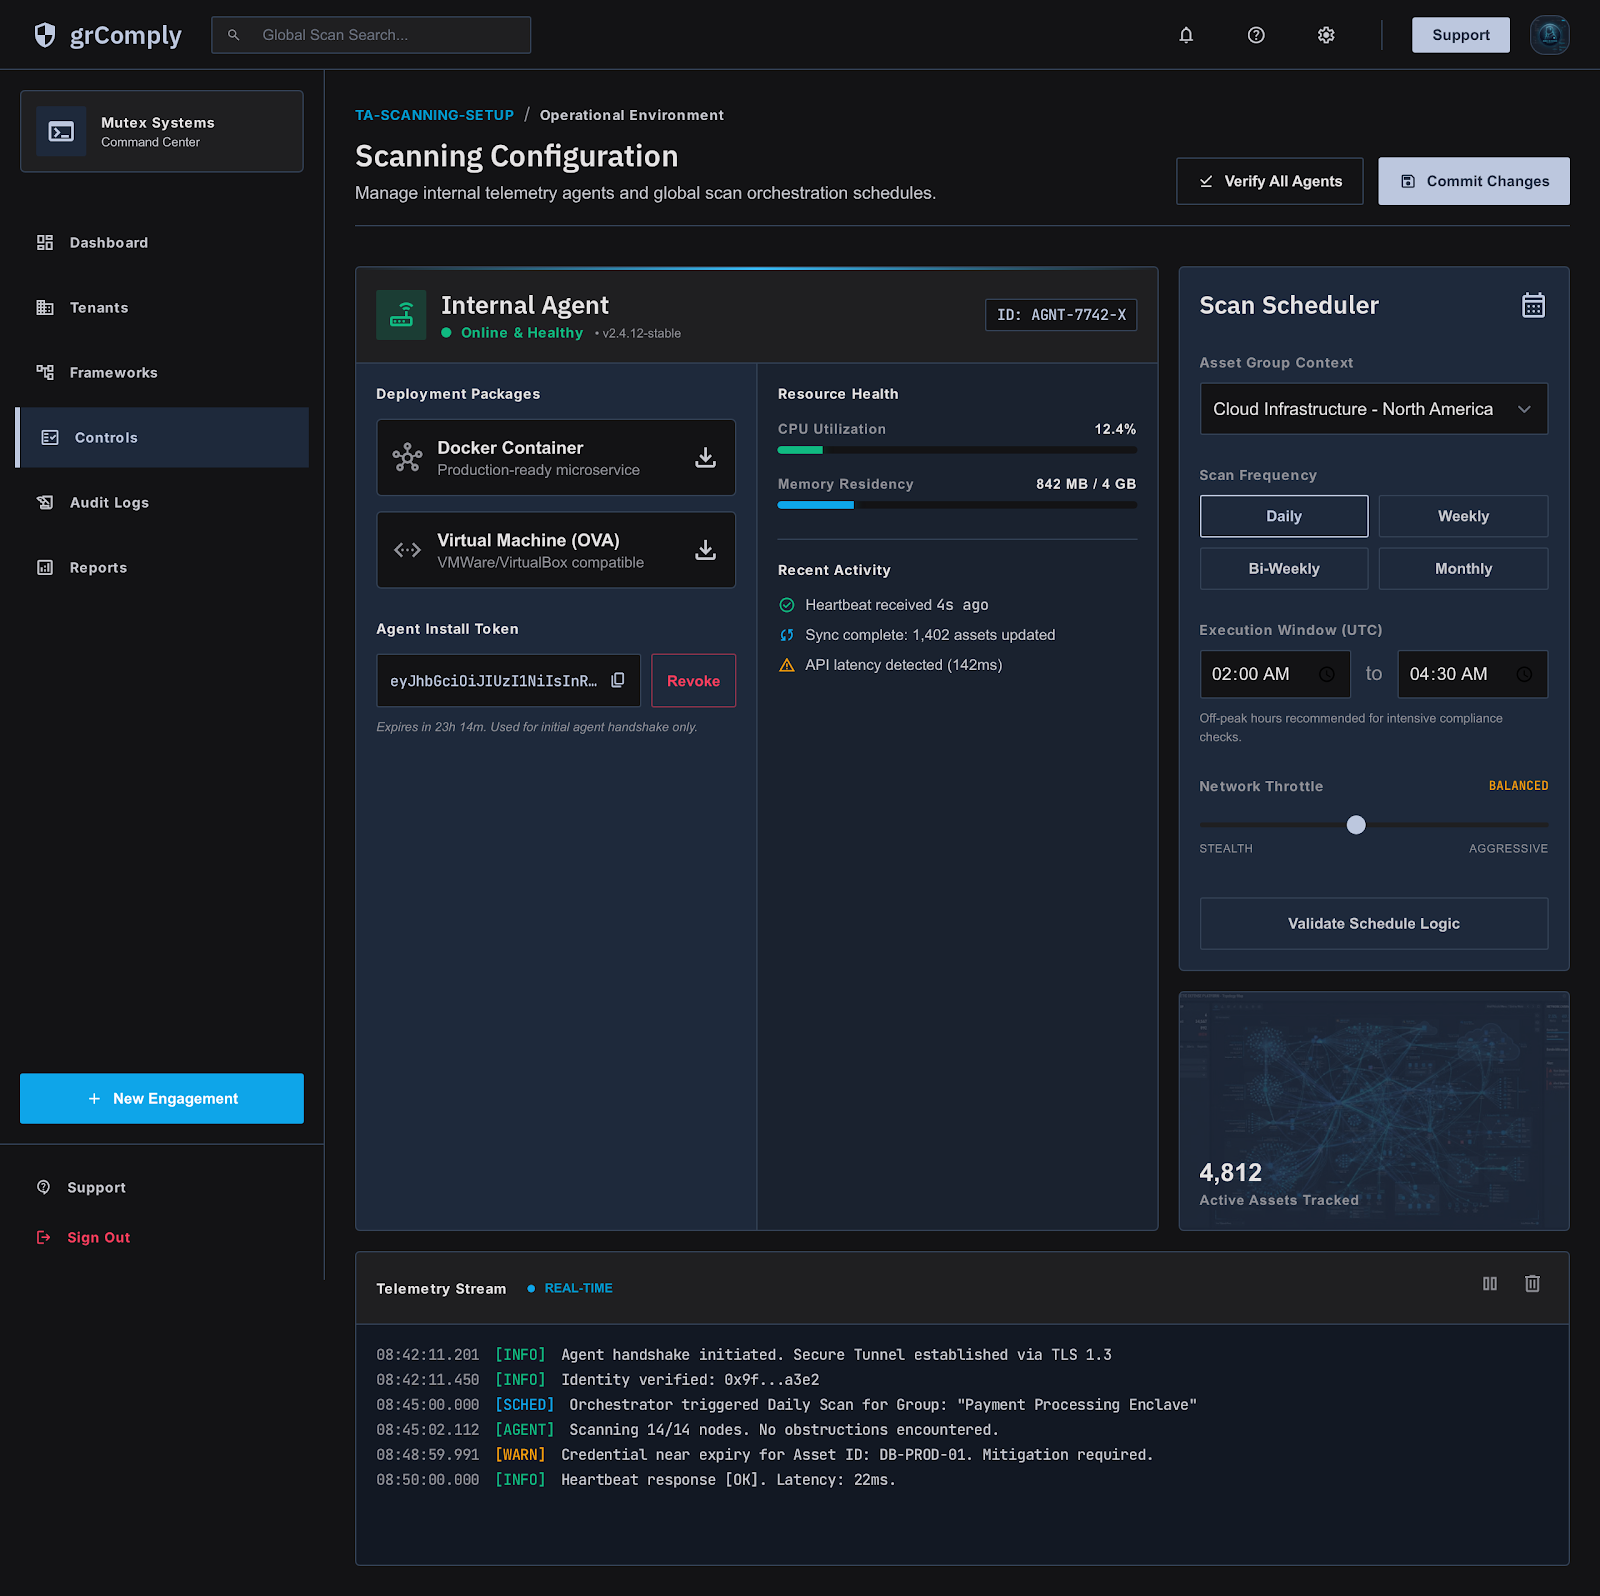
grComply runs agentless external checks and internal agent scans across asset groups on a schedule, enriching results with NVD, OSV, and CISA KEV context so triage starts informed rather than blind. Findings land in one register, link to the asset and its named owner, get triaged by severity, and map straight into the control tree and risk register.
Risk register
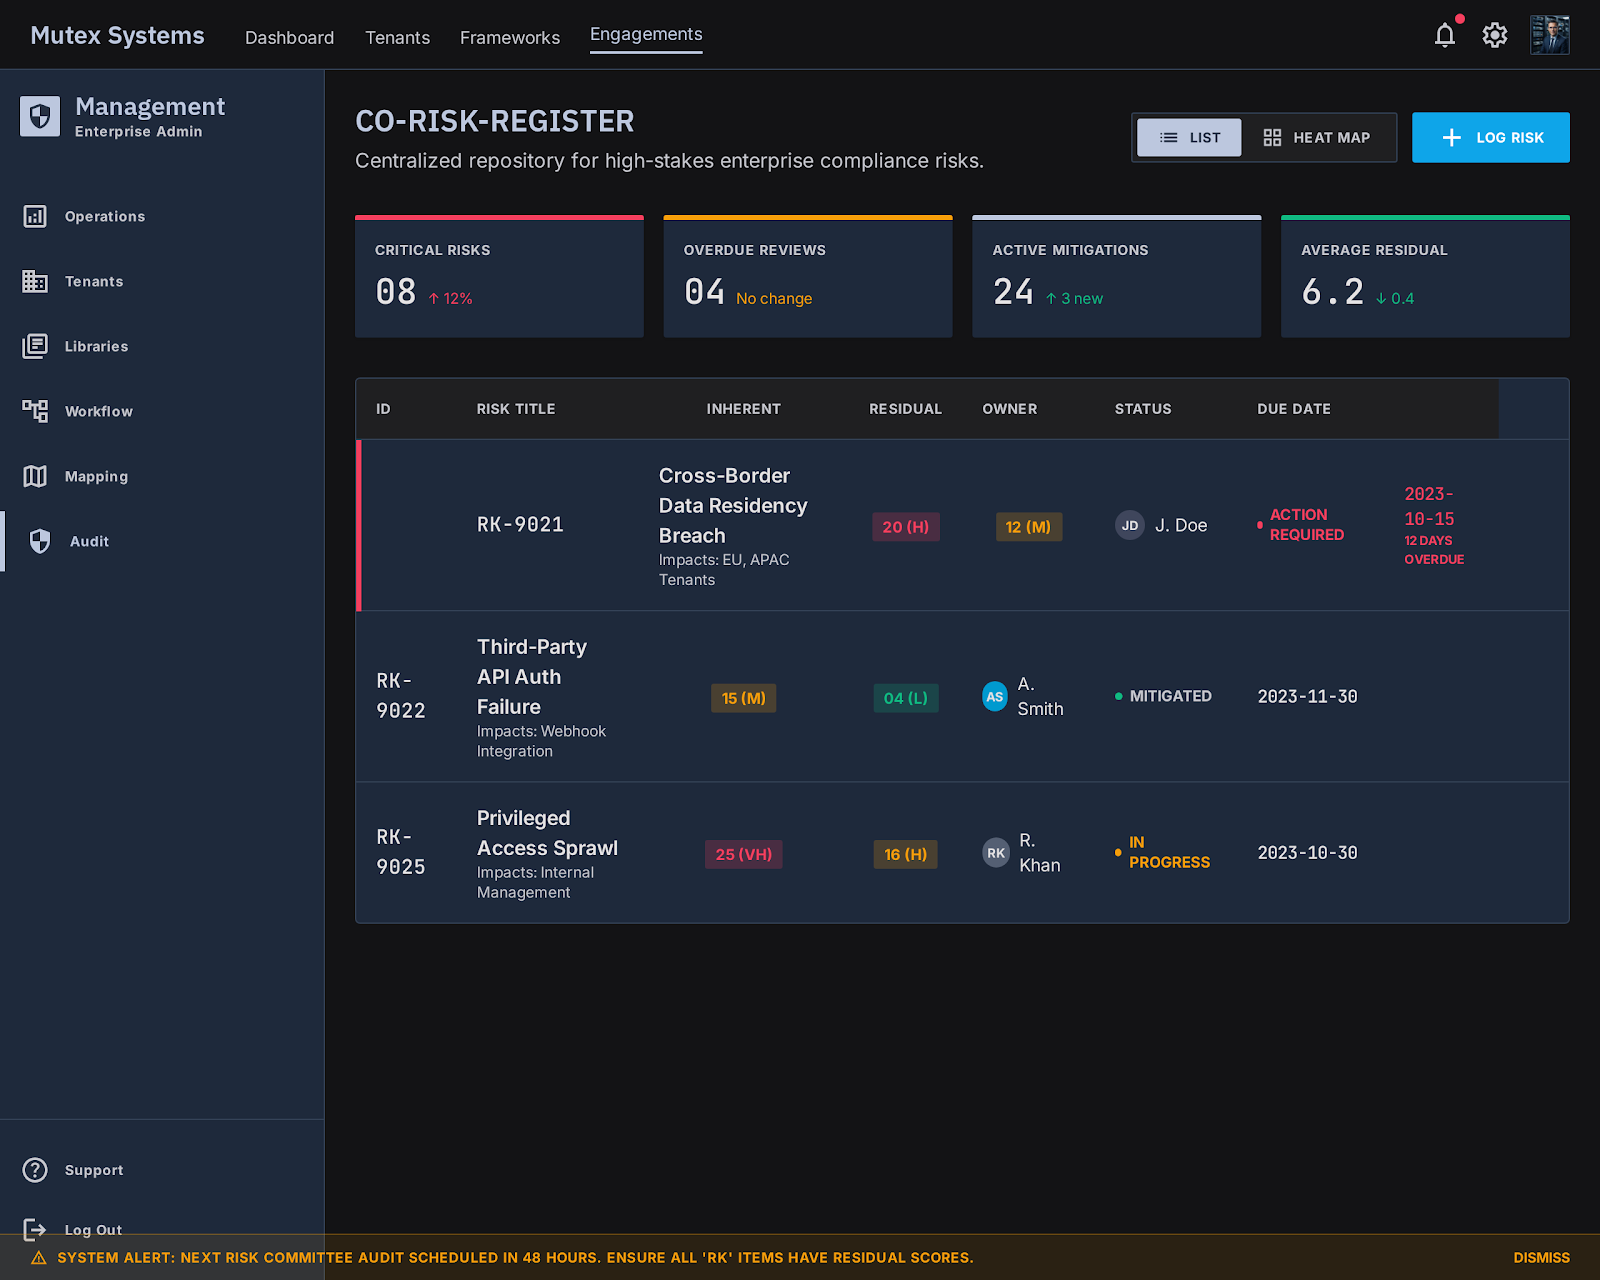
Configure your own scoring methodology — matrix size, weights, appetite line and level names — and preview exactly which risks would be rescored before you save. The register and executive heat map stay aligned, risks link back from findings and controls, and executive acceptance is recorded with rationale, not parked in a slide deck nobody revisits.
Audit delivery
Auditors get a purpose-built engagement home: raise, respond to, and close observations with a full timeline, peer reviewers countersign, and completed engagements produce versioned audit report packages.
Security posture management
One view of your security posture across every scanning engine: an asset inventory with named owners, registered devices checked against configuration baselines, code and configuration scanning, and gaps raised automatically to the accountable person. Full security posture management is part of the Enterprise Cloud, Enterprise and Enterprise Assured plans; vulnerability scanning and findings are on every plan.
Policies, obligations and regulatory change
Draft, review, approve and publish policies with a full approval trail. Track legal and regulatory obligations, link each to the controls that satisfy it, and log regulatory changes so their effect on your programme is assessed and recorded rather than lost in an inbox.
Privacy and AI governance
Run data protection impact assessments (DPIAs) with approval and linked risks, and keep an AI system register — each AI system's purpose, dependencies, linked controls and assets — ready for ISO/IEC 42001 and AI regulation reviews.
AI assistant and policy search
Ask about your compliance programme in plain language. Answers come from your own workspace and link to the controls, evidence, findings or policies they used; policy search answers "do we have a policy that covers this?" from published policies only. Every answer is a draft for a person to review, and the assistant never changes a status.
Reporting and audit trail
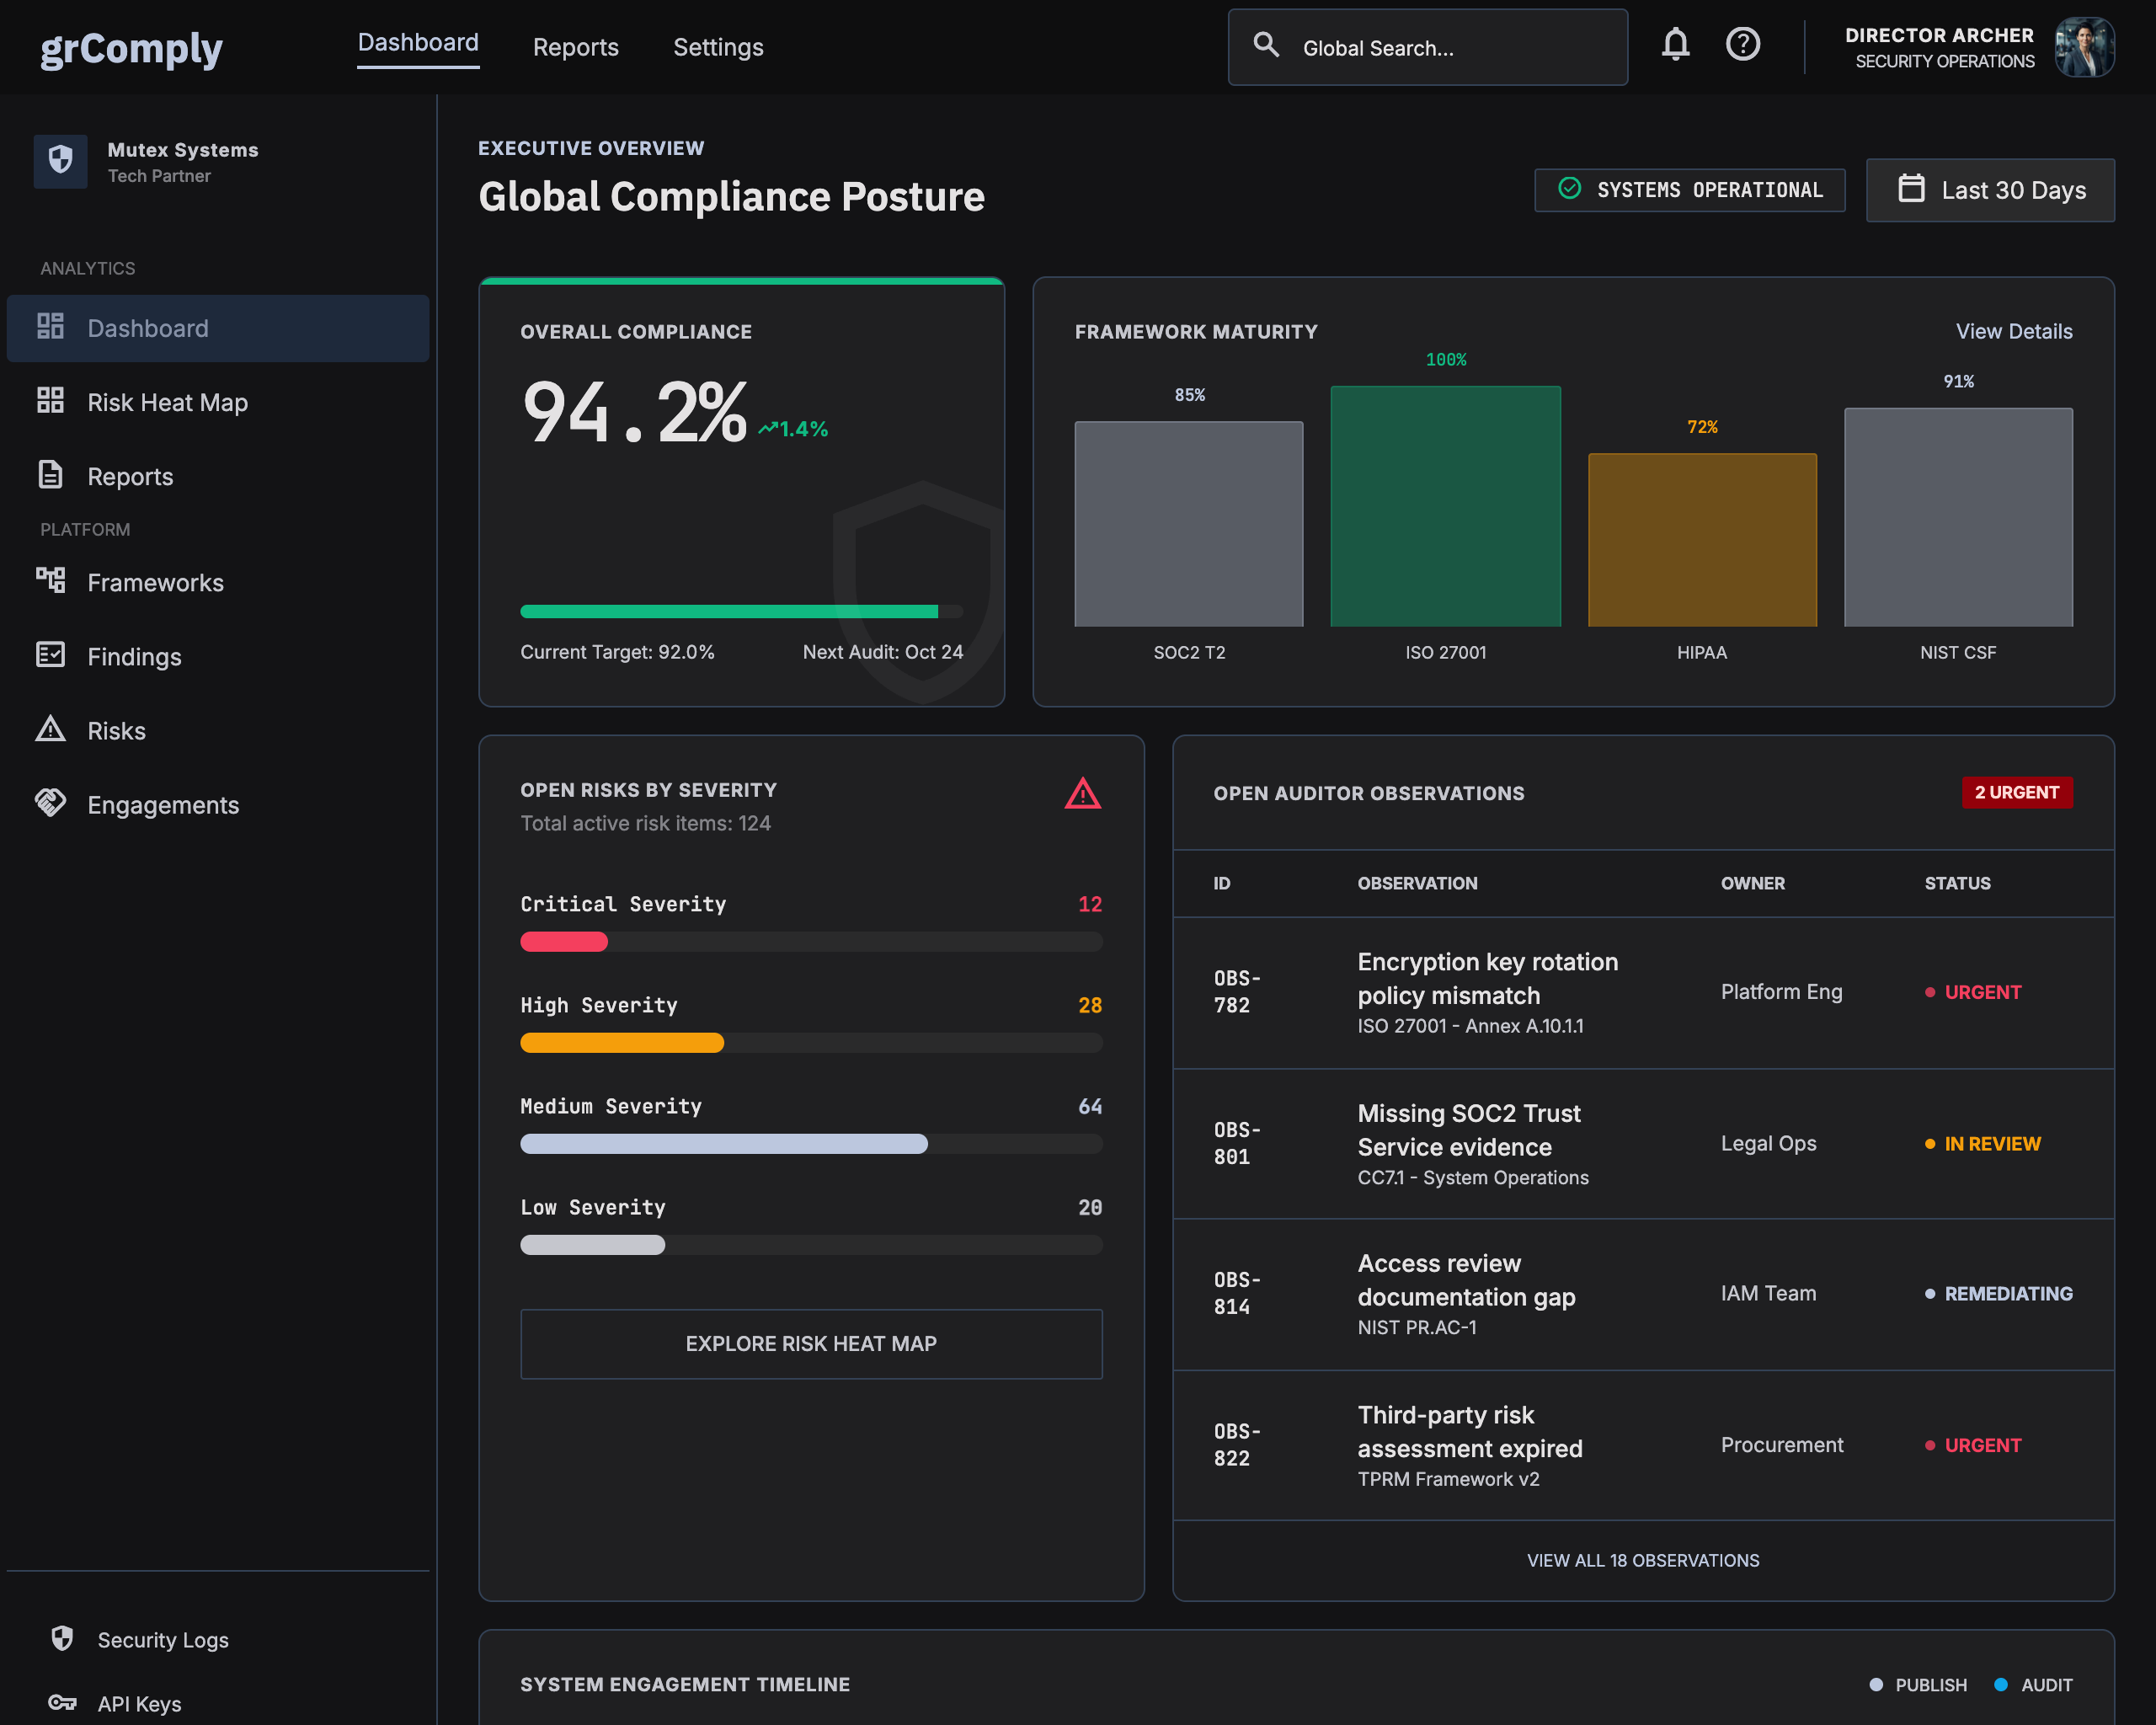
An executive dashboard for leadership, scheduled reports, signed export packages for auditors and regulators, and a tamper-evident audit trail recording who changed what and when — kept for one to seven years depending on plan.
Security awareness training & LMS
Every course needs a stated purpose and a compliance-framework mapping before it can publish, and completion rolls into the same readiness figure as every other control. Campaigns by team, a course player with quick checks and a final test, certificates, coverage against a target, and phishing simulation with team-level results — licensed as training seats separate from platform users, as an add-on on Professional, Enterprise Cloud and Enterprise and included on Enterprise Assured.
Explore security awareness training →One product line, three postures
Deployment posture is not negotiable for regulated organisations — grComply meets you where your data has to live.
Fastest to start
Full feature set on Mutex-managed UK/EU infrastructure, with in-country hosting on Enterprise Cloud. Plans: Starter, Professional, Enterprise Cloud.
Sensitive data stays local
Summaries and configuration sync outbound, with category controls deciding exactly what leaves your estate. Plans: Enterprise, Enterprise Assured.
Fully air-gapped
Licence activation and offline renewal — for regulated estates where nothing leaves the building. Plans: Enterprise, Enterprise Assured.
Same platform, different jobs
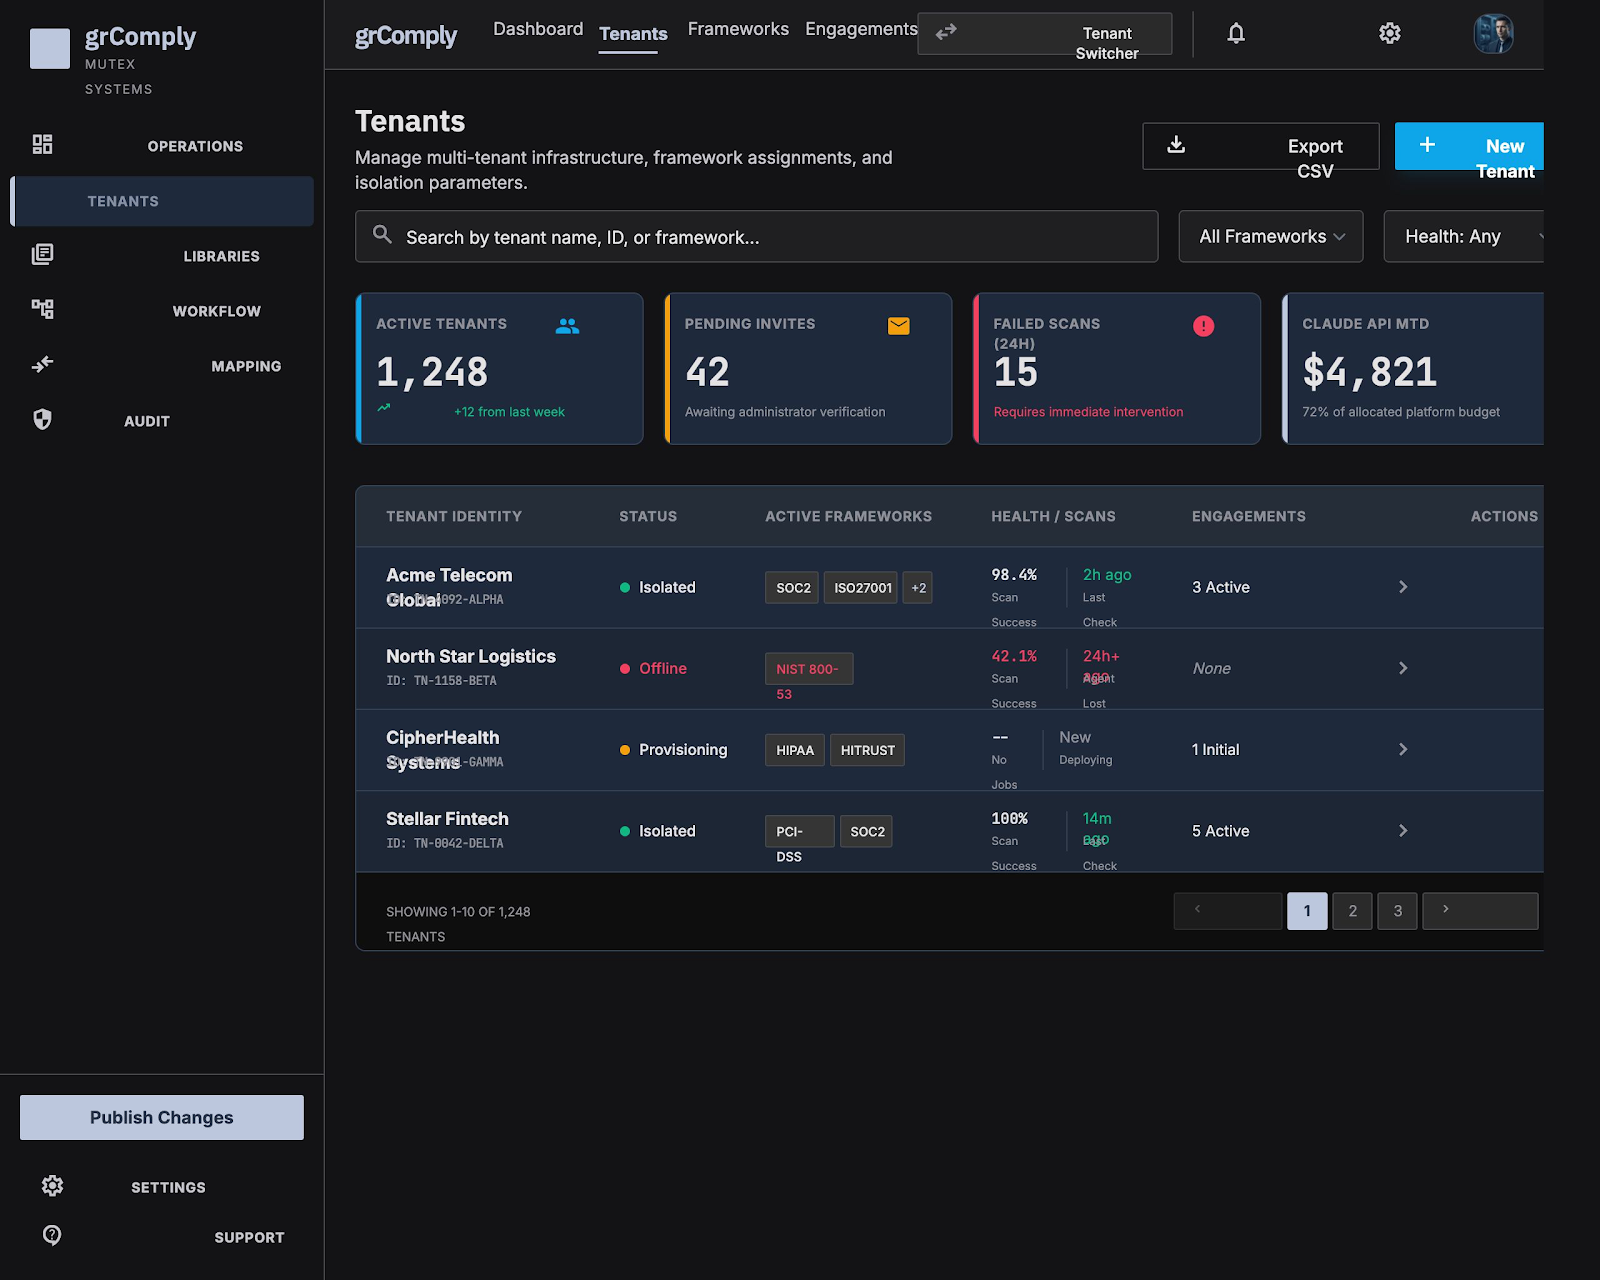
Tenant Admin, Compliance Officer, Executive, Auditor, and Peer Reviewer each land in a purpose-built shell on sign-in — nobody is forced into a dashboard built for someone else's role.
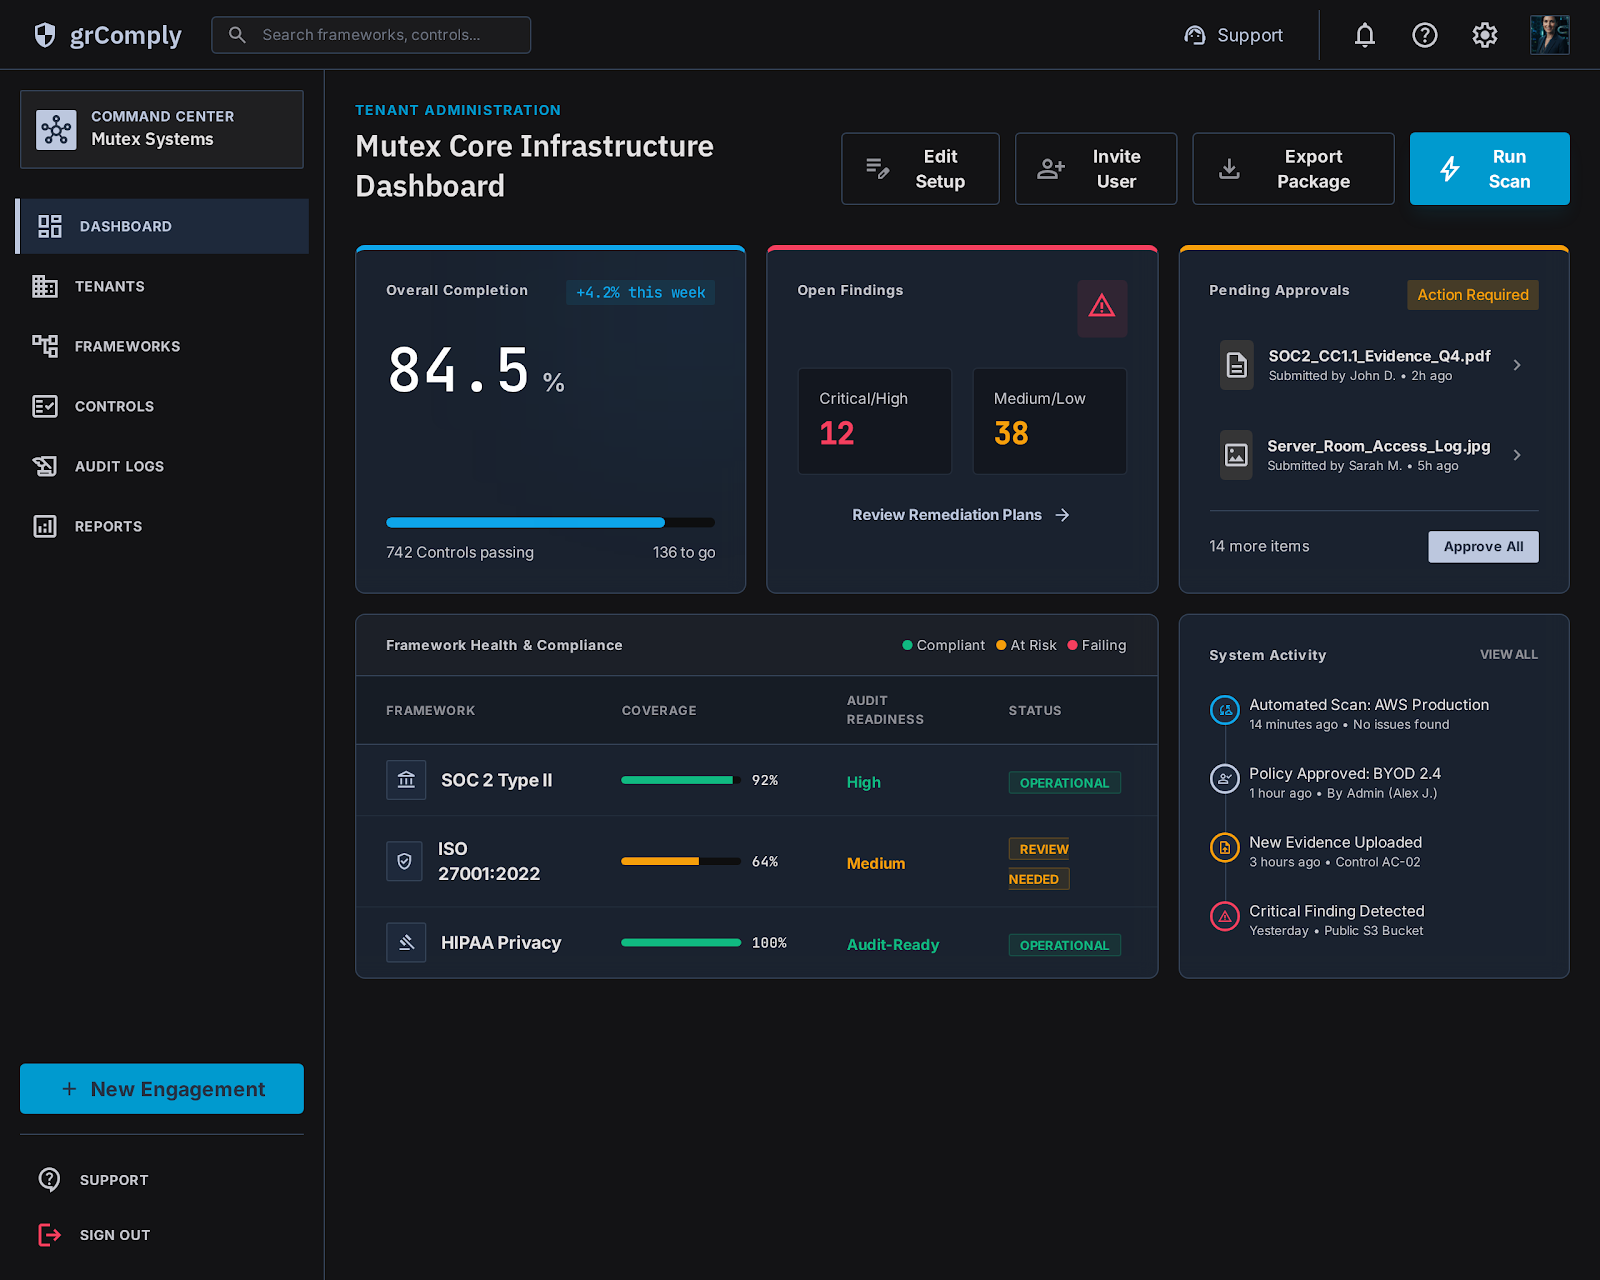
17 screens, captured from the live workspace
Across sign-in, compliance operations, scanning, risk, audit, deployment, and platform administration — not mockups.
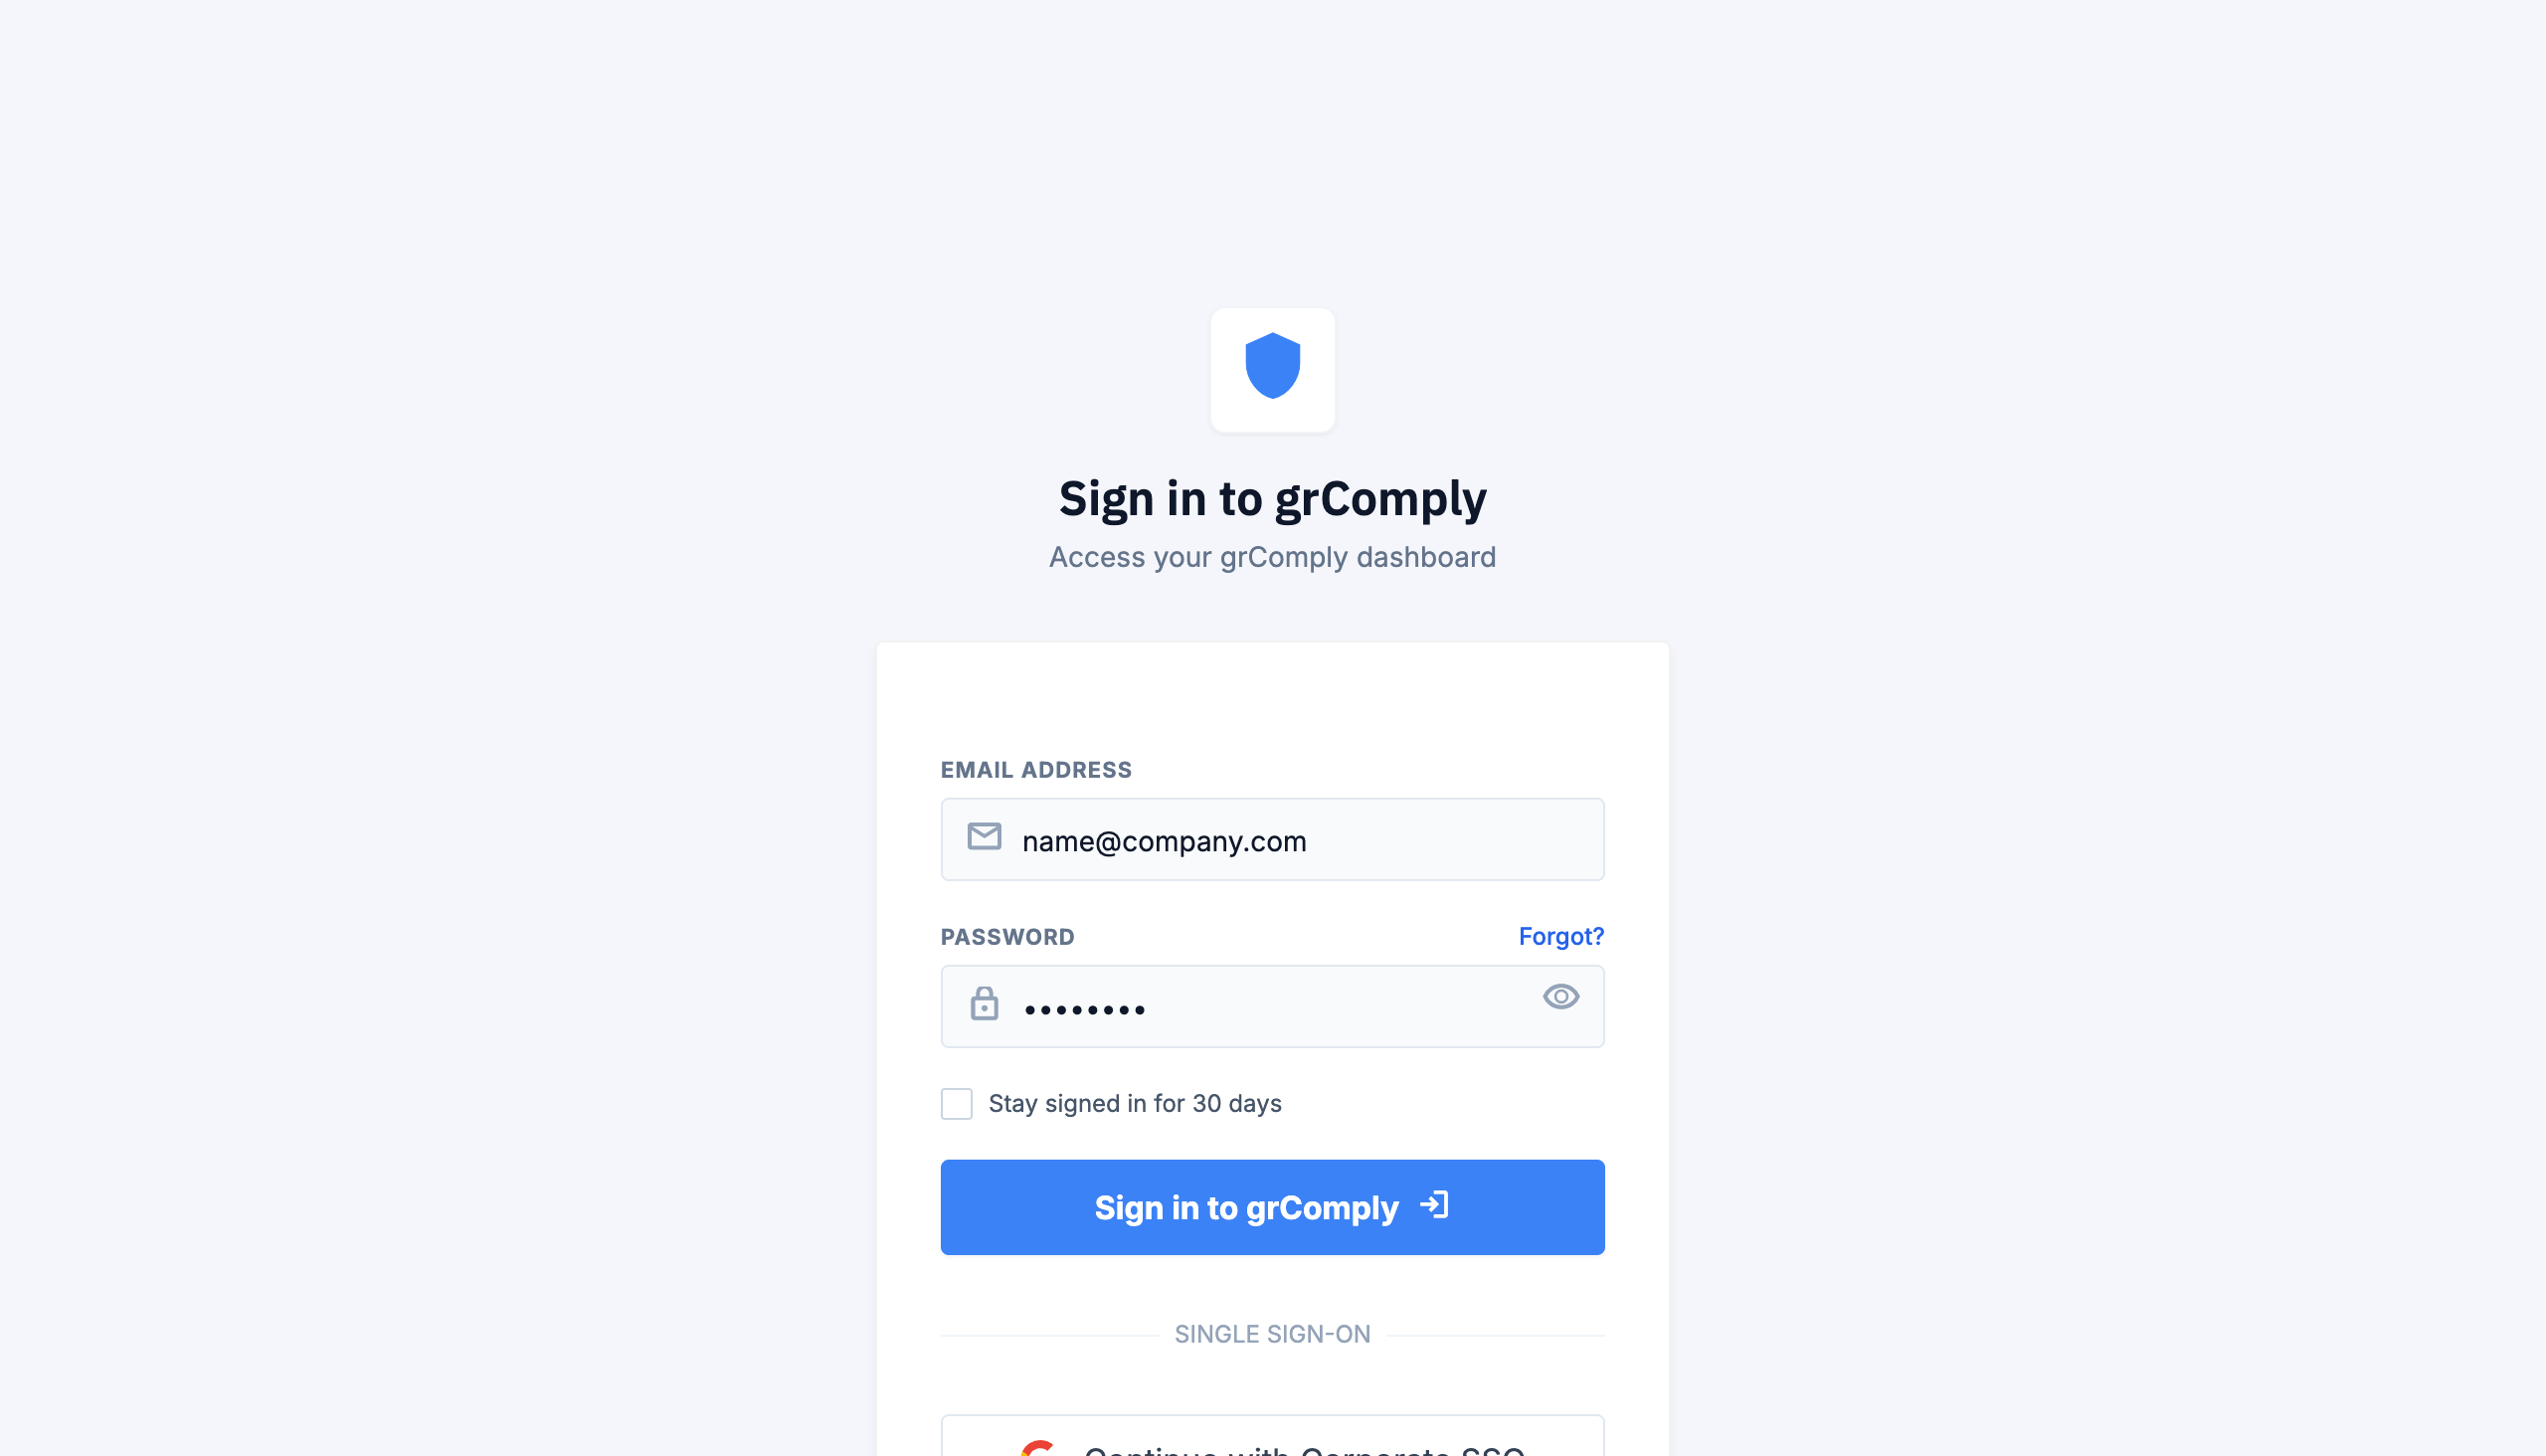
Sign-in
Compliance operations
Scanning & findings
Risk register
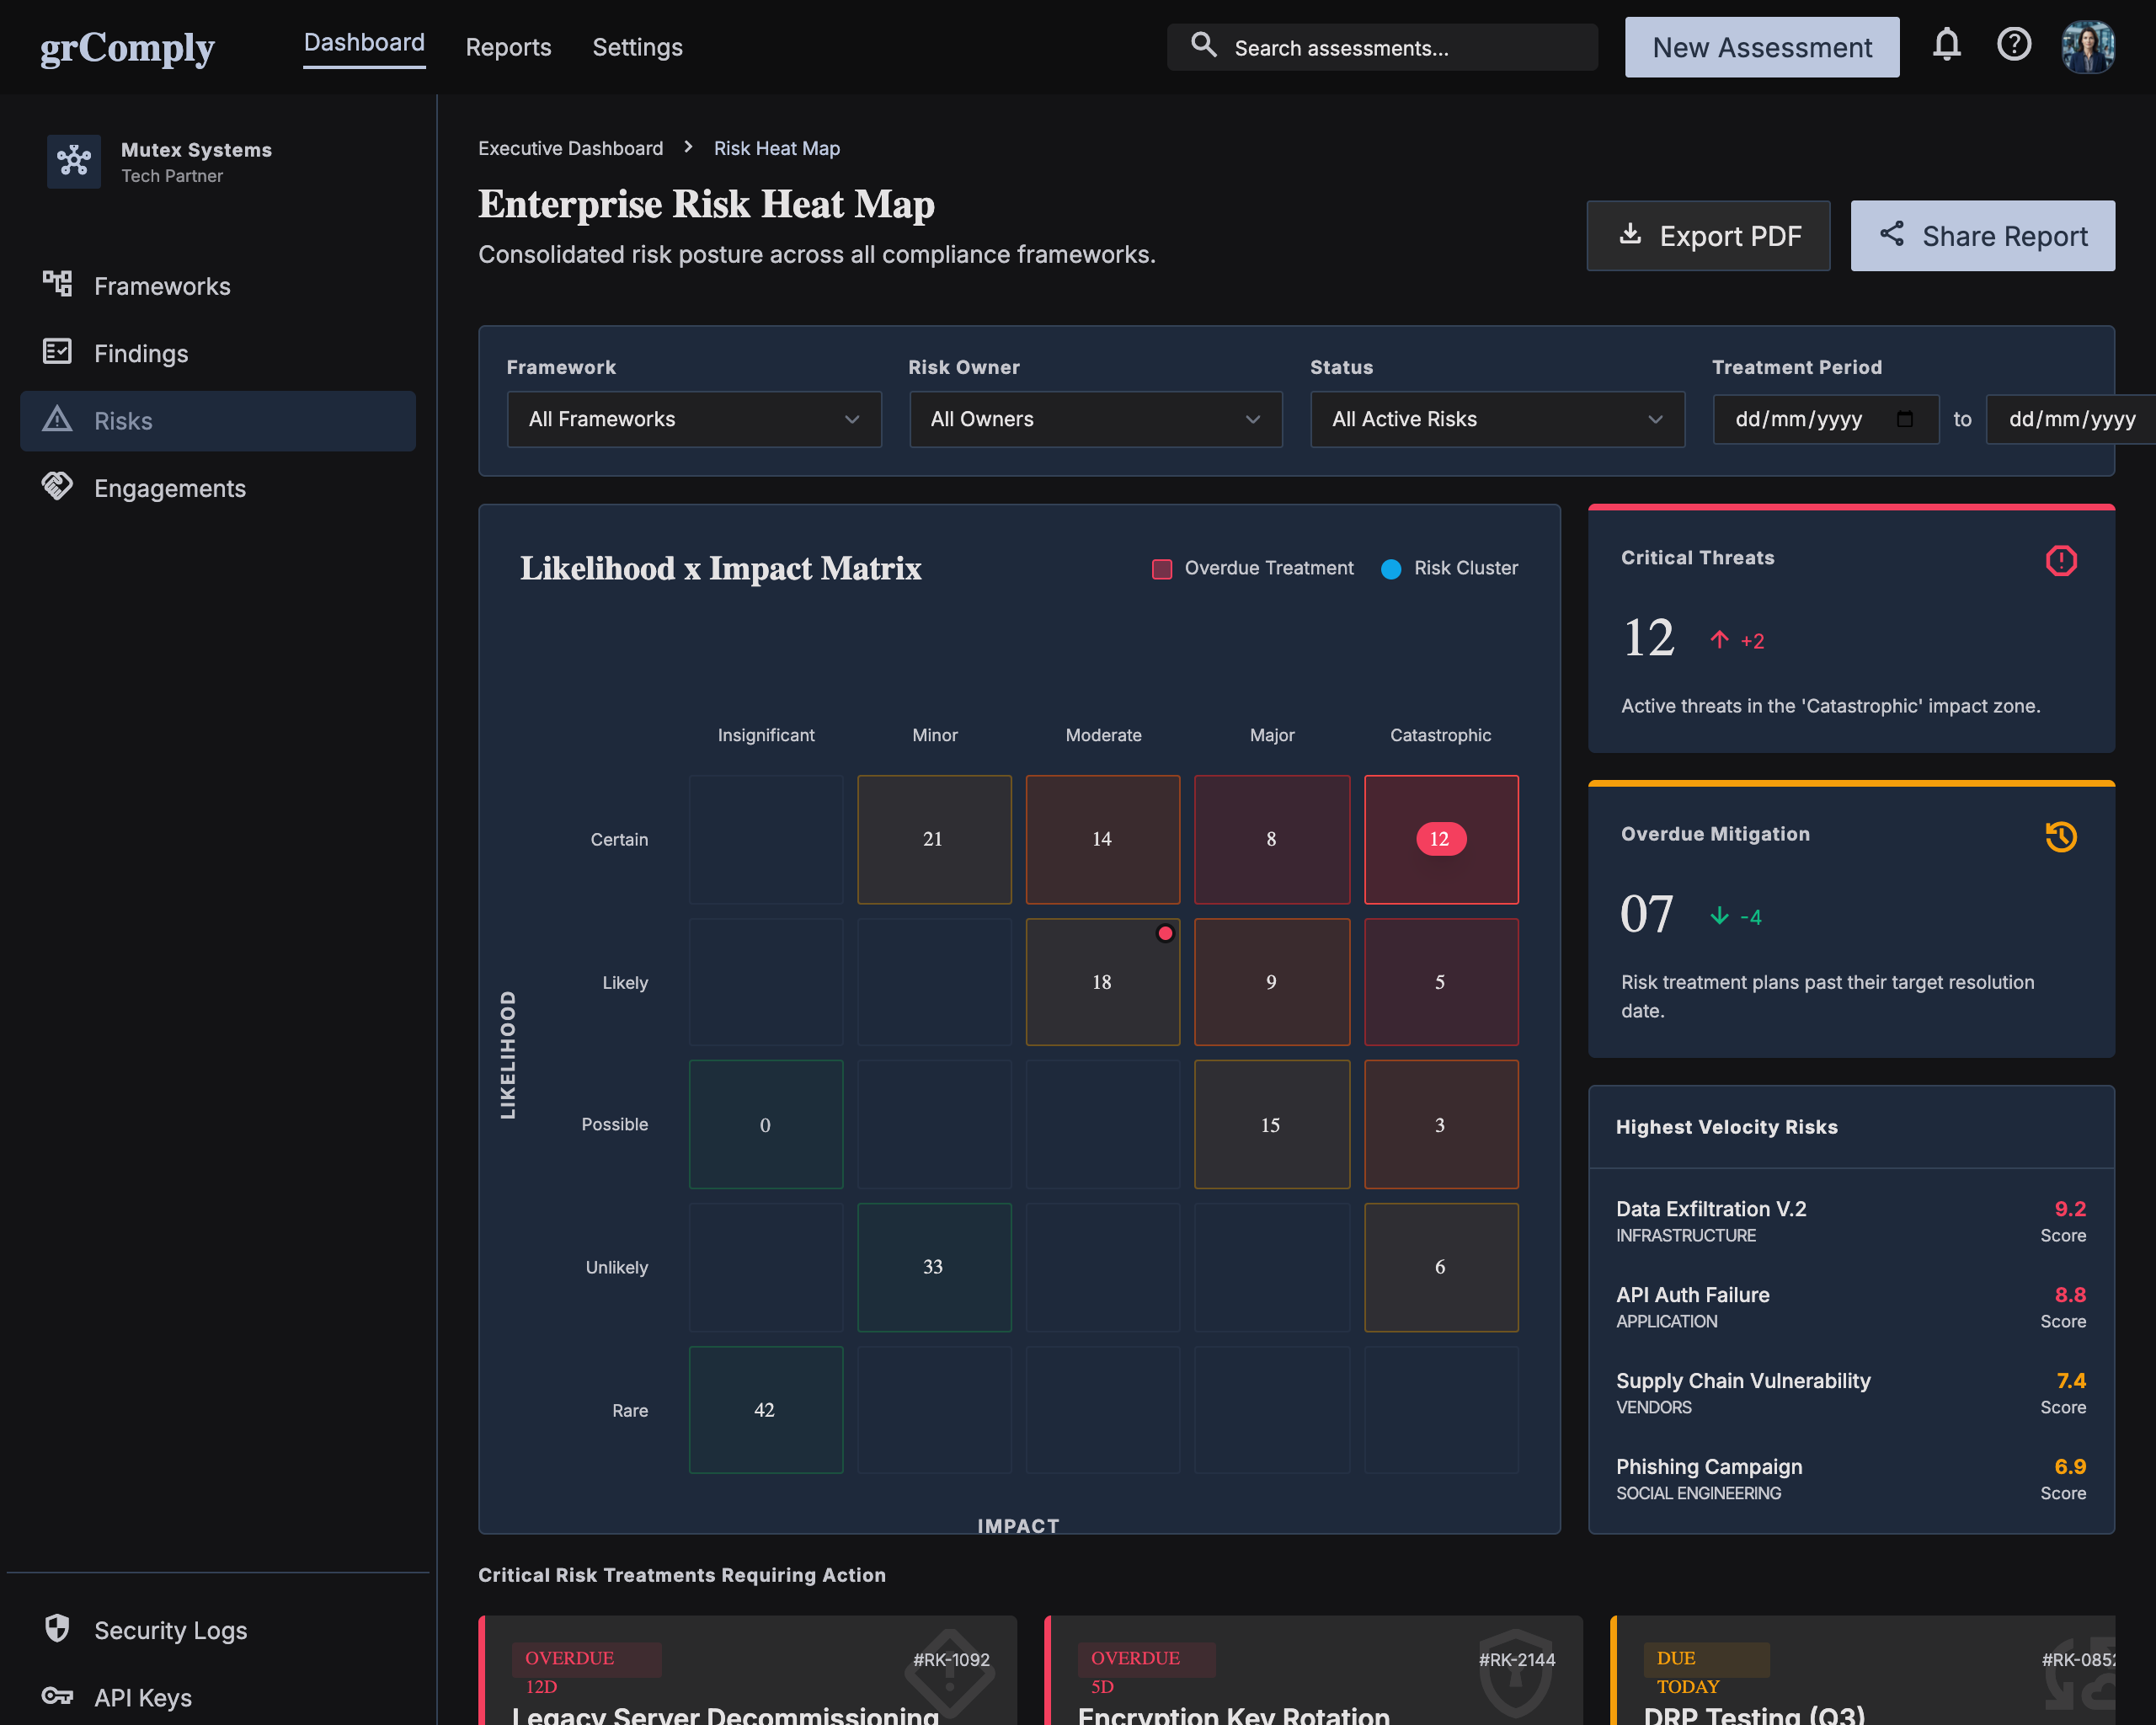
Mapping & executive view
Audit delivery & AI
Deployment
Platform & ops
Getting started
Built for compliance teams under real audit pressure
Compliance and GRC teams preparing for ISO 27001, SOC 2, or sector-specific audits (FCA, State Bank of Pakistan, SECP, PTA, SAMA, and comparable regulators). Consultancies running multi-tenant compliance programmes for several clients from one platform. Regulated organisations that need private on-prem or hybrid deployment rather than pure SaaS. Security teams that want vulnerability scanning and the risk register to feed the same control tree the auditors will review.
Five plans, from cloud to air-gapped
Every plan carries the same compliance core. Plans differ in capacity, hosting, security posture depth and support. Plans start at £1,200 per month, quoted in GBP or USD.
Starter
Cloud (UK/EU). For mid-market organisations running one compliance programme — up to 200 users and 50 frameworks, daily scanning.
Professional
Cloud (UK/EU). For several programmes — up to 500 users and 100 frameworks, scanning every 6 hours, awareness training as an add-on.
Enterprise Cloud
Cloud in UK/EU or in-country. Unlimited frameworks, full security posture management, 7-year audit history and remote onboarding.
Enterprise
Hybrid or fully on-premises, with an air-gapped option and a private AI model option — for banks, telecoms and government.
Enterprise Assured
Enterprise, delivered and supported by Mutex: implementation, 24/7 support, a named customer success manager and quarterly compliance reviews.
Demo and proof of concept
See a working workspace in 30 minutes, then run a proof of concept on your own frameworks and systems before choosing a plan.
Common questions about grComply
What is a GRC platform?
A GRC platform is software that manages Governance, Risk, and Compliance in one system — control inventories, evidence, risk registers, and audit workflow — replacing spreadsheets and disconnected tools with a single source of truth auditors and executives can both trust.
Can grComply run on-premise?
Yes. On the Enterprise and Enterprise Assured plans grComply runs in hybrid mode or fully on-premises, including an air-gapped option, with licence activation and offline renewal for regulated estates that cannot use cloud infrastructure.
How does cross-framework control mapping work?
Controls live in one shared tree. When a control satisfies requirements in NIST, CIS, SOC 2, or a tenant-specific framework simultaneously, grComply maps it once and shows coverage across all adopted frameworks in a matrix — including an impact preview before you adopt a new framework version.
Does grComply use AI to auto-complete compliance work?
No. grComply's AI assistant answers questions from your own workspace, names the records it relied on, and drafts narratives and responses on request — always labelled as a draft. A person confirms before any control status changes; grComply never treats machine-generated text as verified evidence.
How do you prepare evidence for a SOC 2 audit in grComply?
Upload evidence against the specific control requirement, route it through the approval path, and it versions automatically as you update it. The completion cache updates live, reflecting current evidence state rather than a stale export.
Which grComply plan is right for us?
grComply has five plans. Starter, Professional and Enterprise Cloud run in the cloud and scale in users, frameworks and scanning frequency. Enterprise and Enterprise Assured run hybrid or on-premises; Enterprise Assured adds implementation, 24/7 support and quarterly compliance reviews. Plans start at £1,200 per month.
How do I get a grComply demo or proof of concept?
Contact us or book a 30-minute meeting on this page. A product specialist shows a working grComply workspace, and can scope a proof of concept on your own frameworks and systems before you choose a plan. Quotes are provided in GBP or USD.
What's the difference between cloud and hybrid deployment?
Cloud runs the full feature set on Mutex-managed UK/EU infrastructure — the Starter, Professional and Enterprise Cloud plans. Hybrid, on the Enterprise plans, keeps sensitive data on your own infrastructure while chosen summaries sync outbound, with category controls deciding exactly what leaves your estate.
See grComply on your own frameworks
Contact us for a demo, proof of concept or pricingPowered by Mutex Systems — engagement-grade GRC workflow with Mutex Systems as the platform provider. Explore the full SaaS portfolio →
Contact us for a demo, proof of concept or pricing
Tell us about your frameworks and deployment posture — cloud, hybrid, or private on-prem — and we'll route it to the right product specialist.
- A product specialist replies personally — not a bot
- No obligation after the first conversation
- WhatsApp support also available 24/7
By submitting, you agree to be contacted about your enquiry. We respect your privacy.
Book a grComply demo
Pick a time that works for you — 30 minutes with a product specialist, no sales script.
Ready to see grComply?
We respond within one working day — or reach us instantly on WhatsApp.