SOC 2 Type II, proven over the whole period.
SOC 2 Type II is an AICPA Trust Services Criteria attestation that tests whether your controls operated effectively across an entire examination period, not just on one date. grComply seeds the identical TSC 2017 structure used for Type I — Security plus Availability, Confidentiality, Processing Integrity, and Privacy — but tracks evidence continuously: scheduled scanning generates dated findings across the period, the completion cache updates live, and a control that lapses mid-period shows as a tracked exception rather than a smoothed-over year-end summary.
What is SOC 2 Type II? SOC 2 Type II is an attestation report that tests whether an organisation's controls both were suitably designed and operated effectively throughout a defined examination period — typically 3 to 12 months. It's the more rigorous companion to Type I, and the report most enterprise buyers and security questionnaires actually ask for.
How grComply benefits your SOC 2 Type II programme
Operating-effectiveness evidence over the whole period
Type II needs proof controls ran throughout an examination window — grComply's live completion cache and dated evidence trail cover the period, not a snapshot.
Continuous scanning matches a continuous examination
Scheduled external/internal scans generate dated findings across the period, exactly what a Type II sample-testing approach expects to see.
Same tree as Type I — no re-authoring
A tenant already running Type I upgrades to Type II on the identical TSC control tree, with evidence history intact.
Exception tracking, not silent gaps
A control that failed mid-period is tracked as a gap with remediation evidence attached, not smoothed over in a year-end summary.
Peer-reviewed, versioned report at period close
The same two-person countersign discipline and versioned report package used for Type I applies across the full examination period.
Cross-framework credit across the same period
Evidence dated within the examination window can simultaneously satisfy an equivalent NIST CSF or ISO 27001 control for the same date range.
5 TSC series, tested for operating effectiveness
The identical Common Criteria plus optional categories as Type I — the difference here is every control needs evidence spanning the whole examination period, not one date.
Security — Common Criteria (CC)
The mandatory baseline — CC1 through CC9 — with evidence sampled across the examination period to prove controls operated continuously, not just at kickoff.
Availability
Uptime and resilience commitments tested with dated incident, monitoring, and recovery evidence spanning the period.
Confidentiality
Confidential-data handling controls tested for consistent operation, not a one-time policy sign-off.
Processing Integrity
Processing correctness evidenced across representative transactions or processing runs throughout the period.
Privacy
Ongoing conformity with the privacy notice, evidenced with dated records of consent, access, and disposal activity.
Evidence grComply already models for SOC 2 Type II
Real evidence-requirement examples from the seeded control library — the same evidence types every other framework in grComply uses, not a bespoke process for this one.
| Control | Evidence type | Example |
|---|---|---|
| CC7.2 — Anomaly detection | SIEM log sample (dated range) | Monitoring evidence spanning the full examination period, not a single snapshot |
| CC6.3 — Access removal | IAM export (periodic) | Joiner-mover-leaver access review evidence sampled at intervals across the period |
| A1.3 — Recovery testing | Procedure / attestation | Backup-restore test evidence dated within the examination window |
| PI1.1 — Processing accuracy | Narrative + sample evidence | Processing-integrity sample testing narrative covering the period |
| P6.1 — Third-party disclosure | Contract document | Data processing agreements current throughout the examination period |
Why this matters: The hardest part of a Type II examination is proving a control didn't just exist once but ran the whole time — grComply's live completion cache and dated evidence trail are built exactly for that continuous-proof problem, not retrofitted onto a point-in-time model.
SOC 2 Type II, in the live workspace
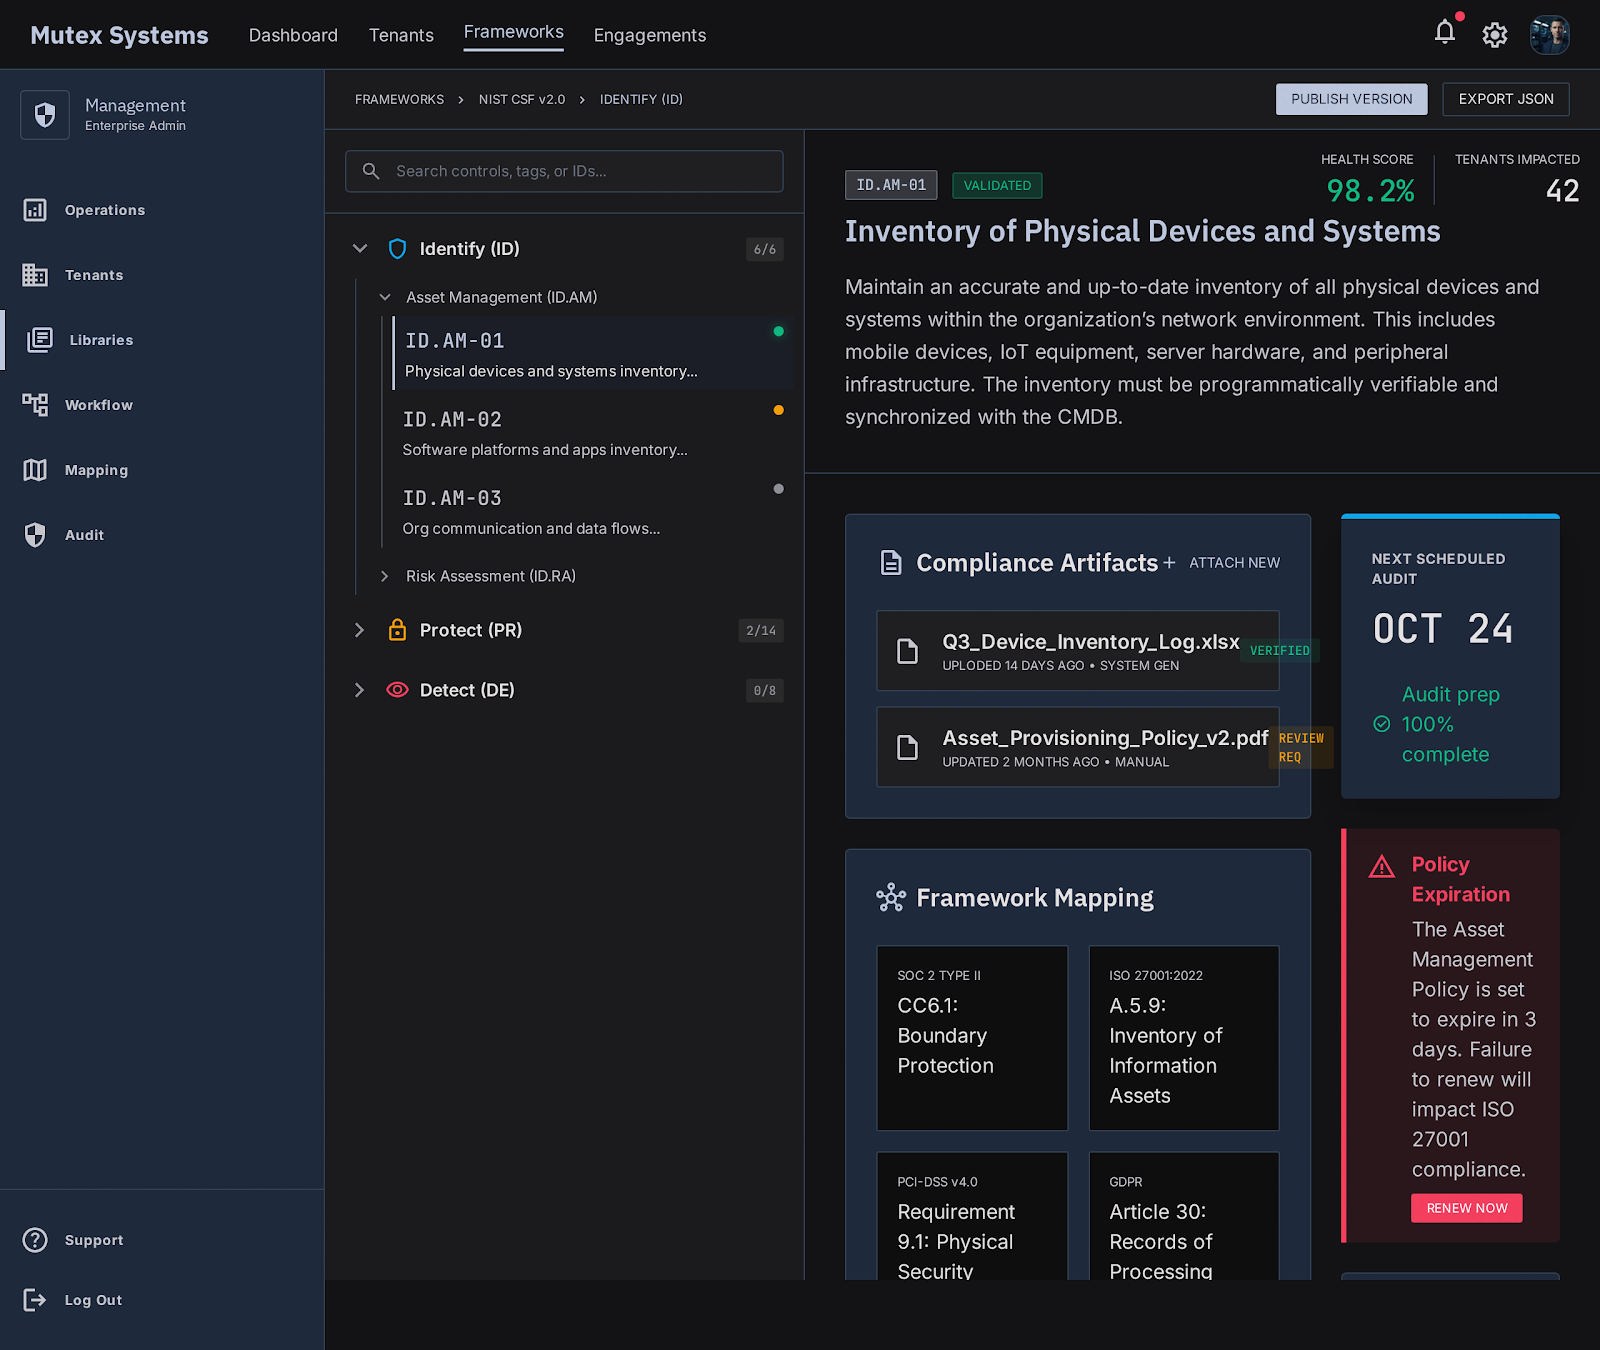
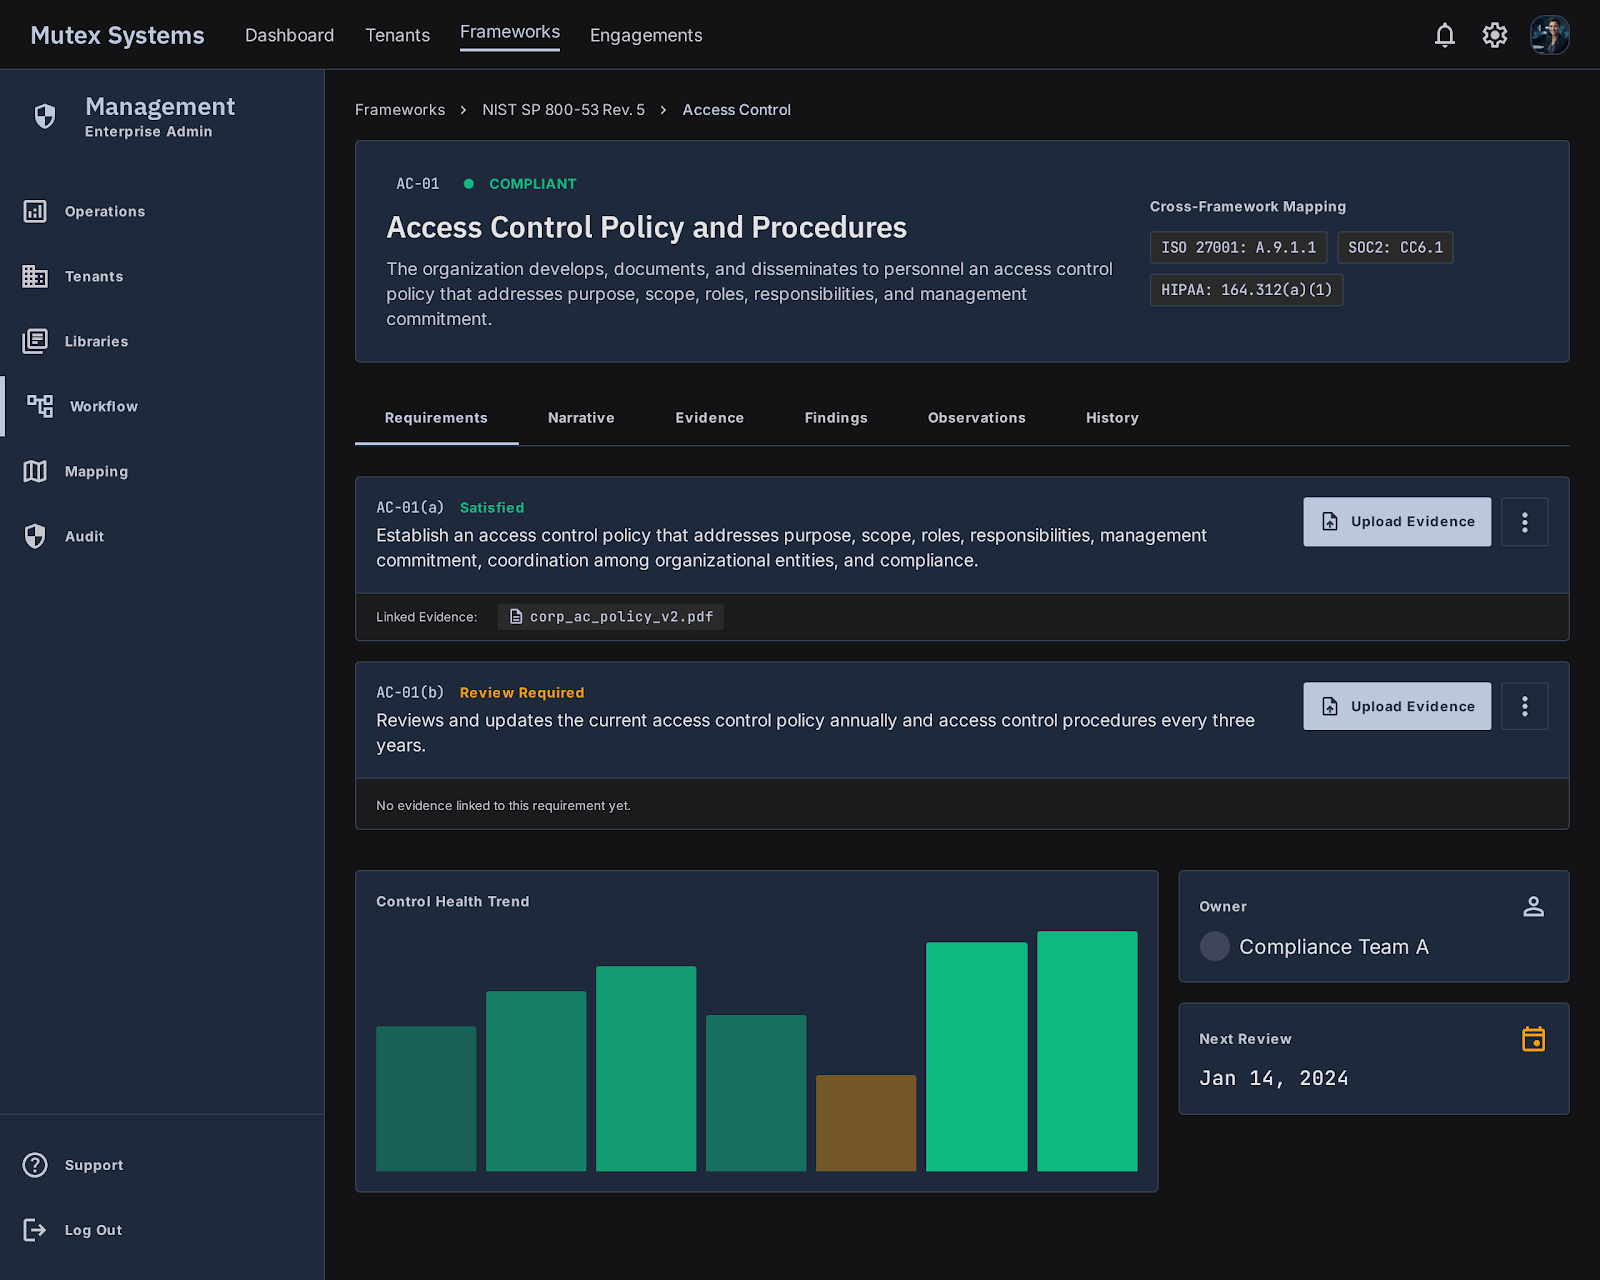
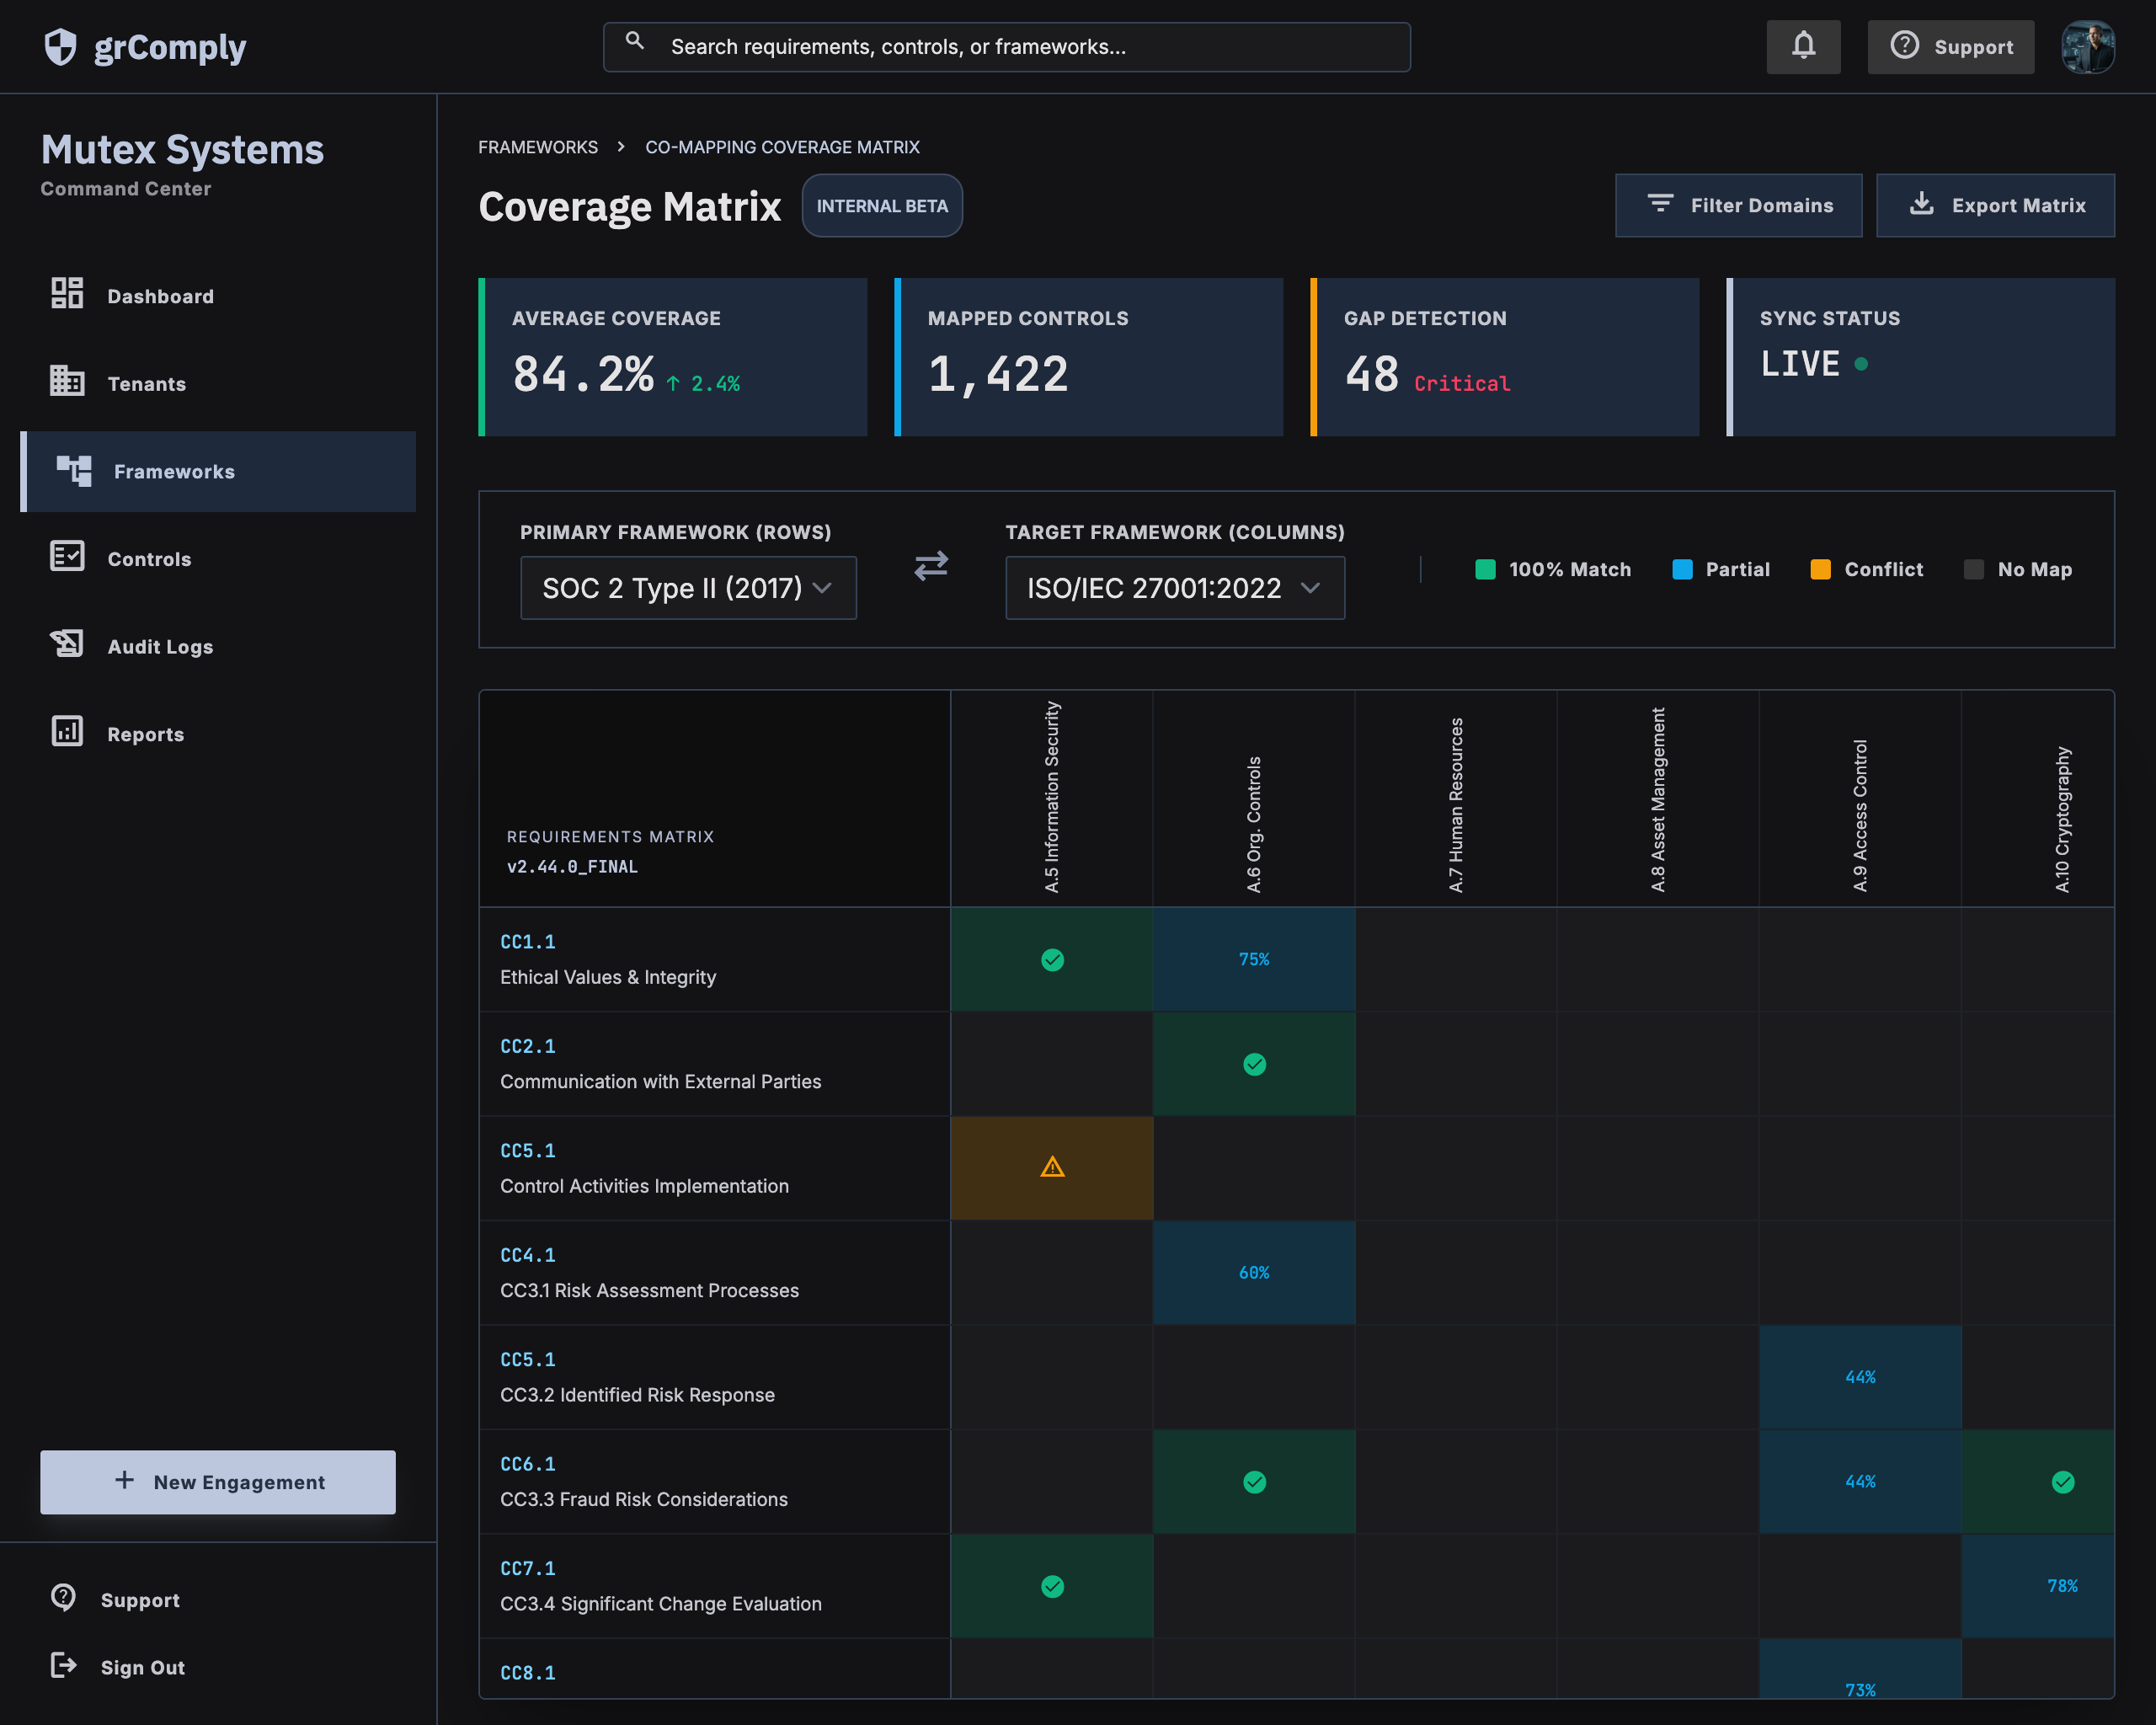
The same grComply workspace shown across the platform — control browser, mapping, evidence, and AI assist apply identically to SOC 2 Type II.
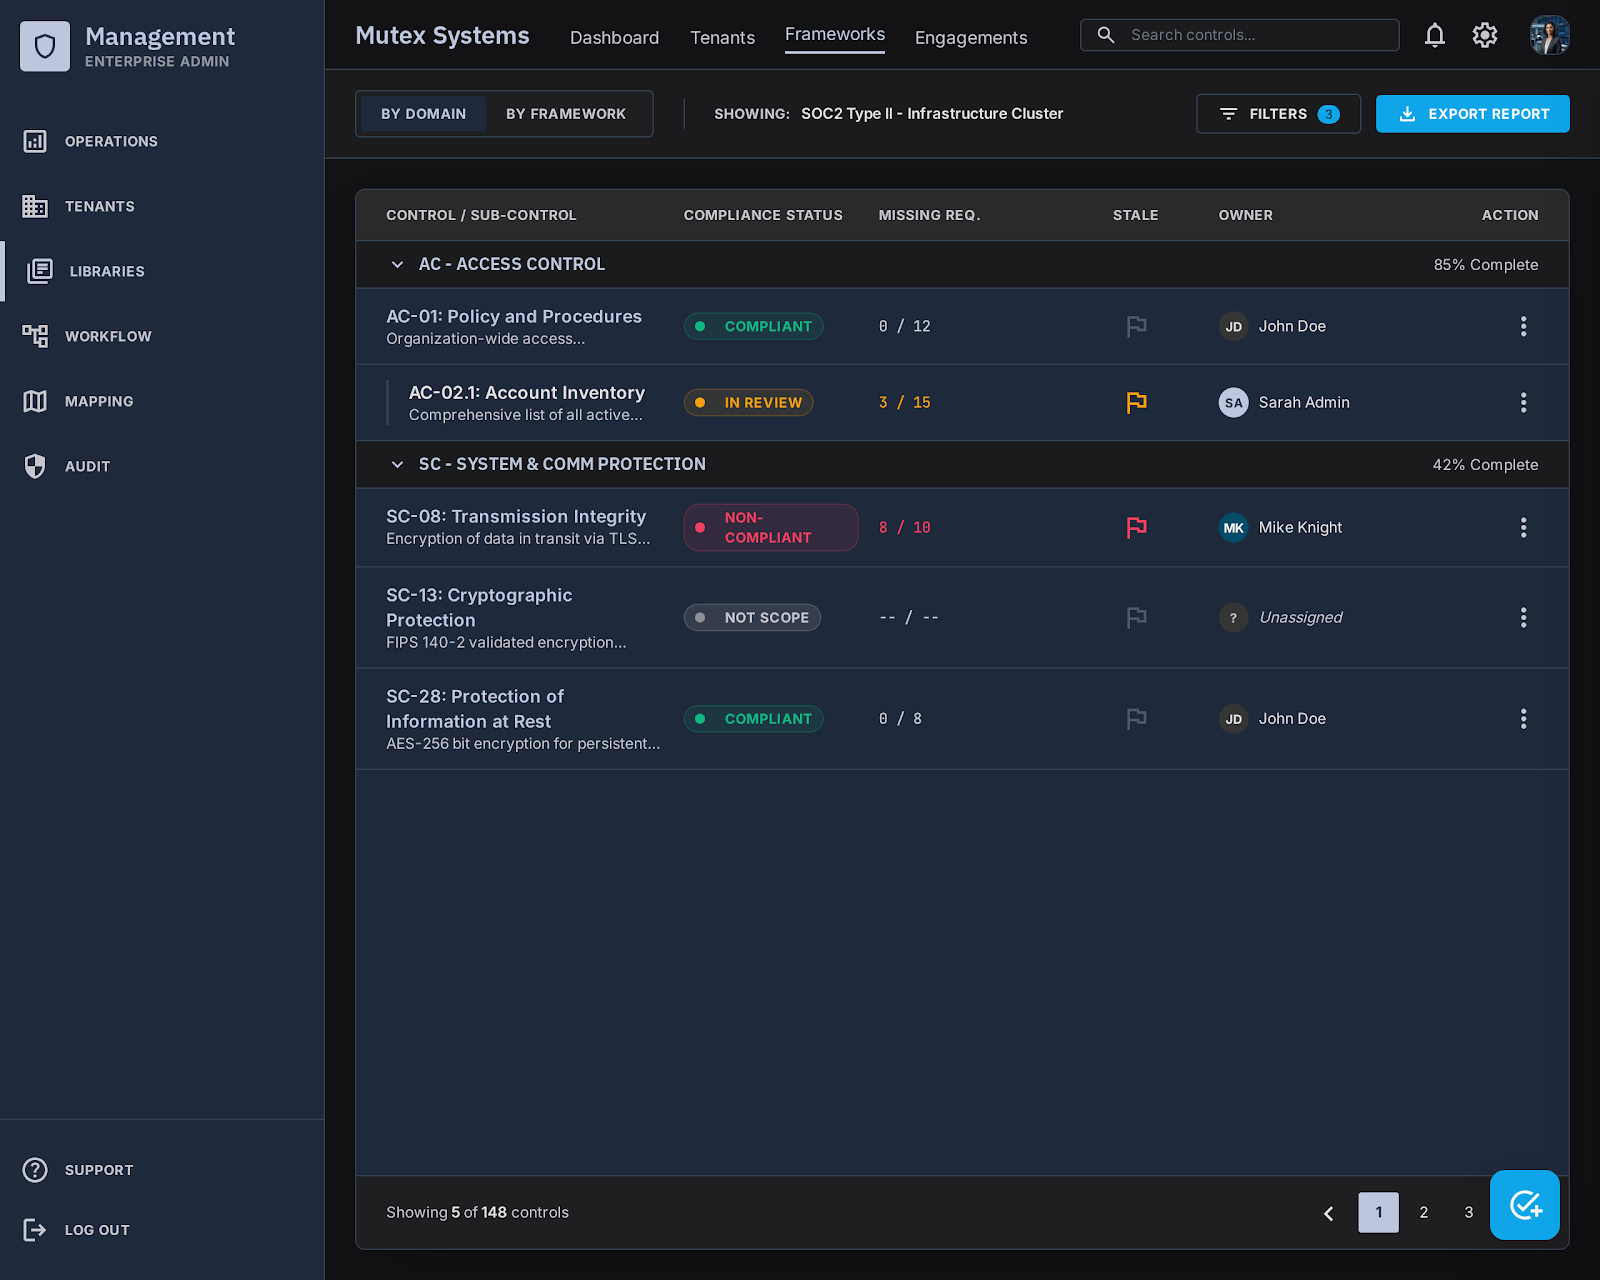
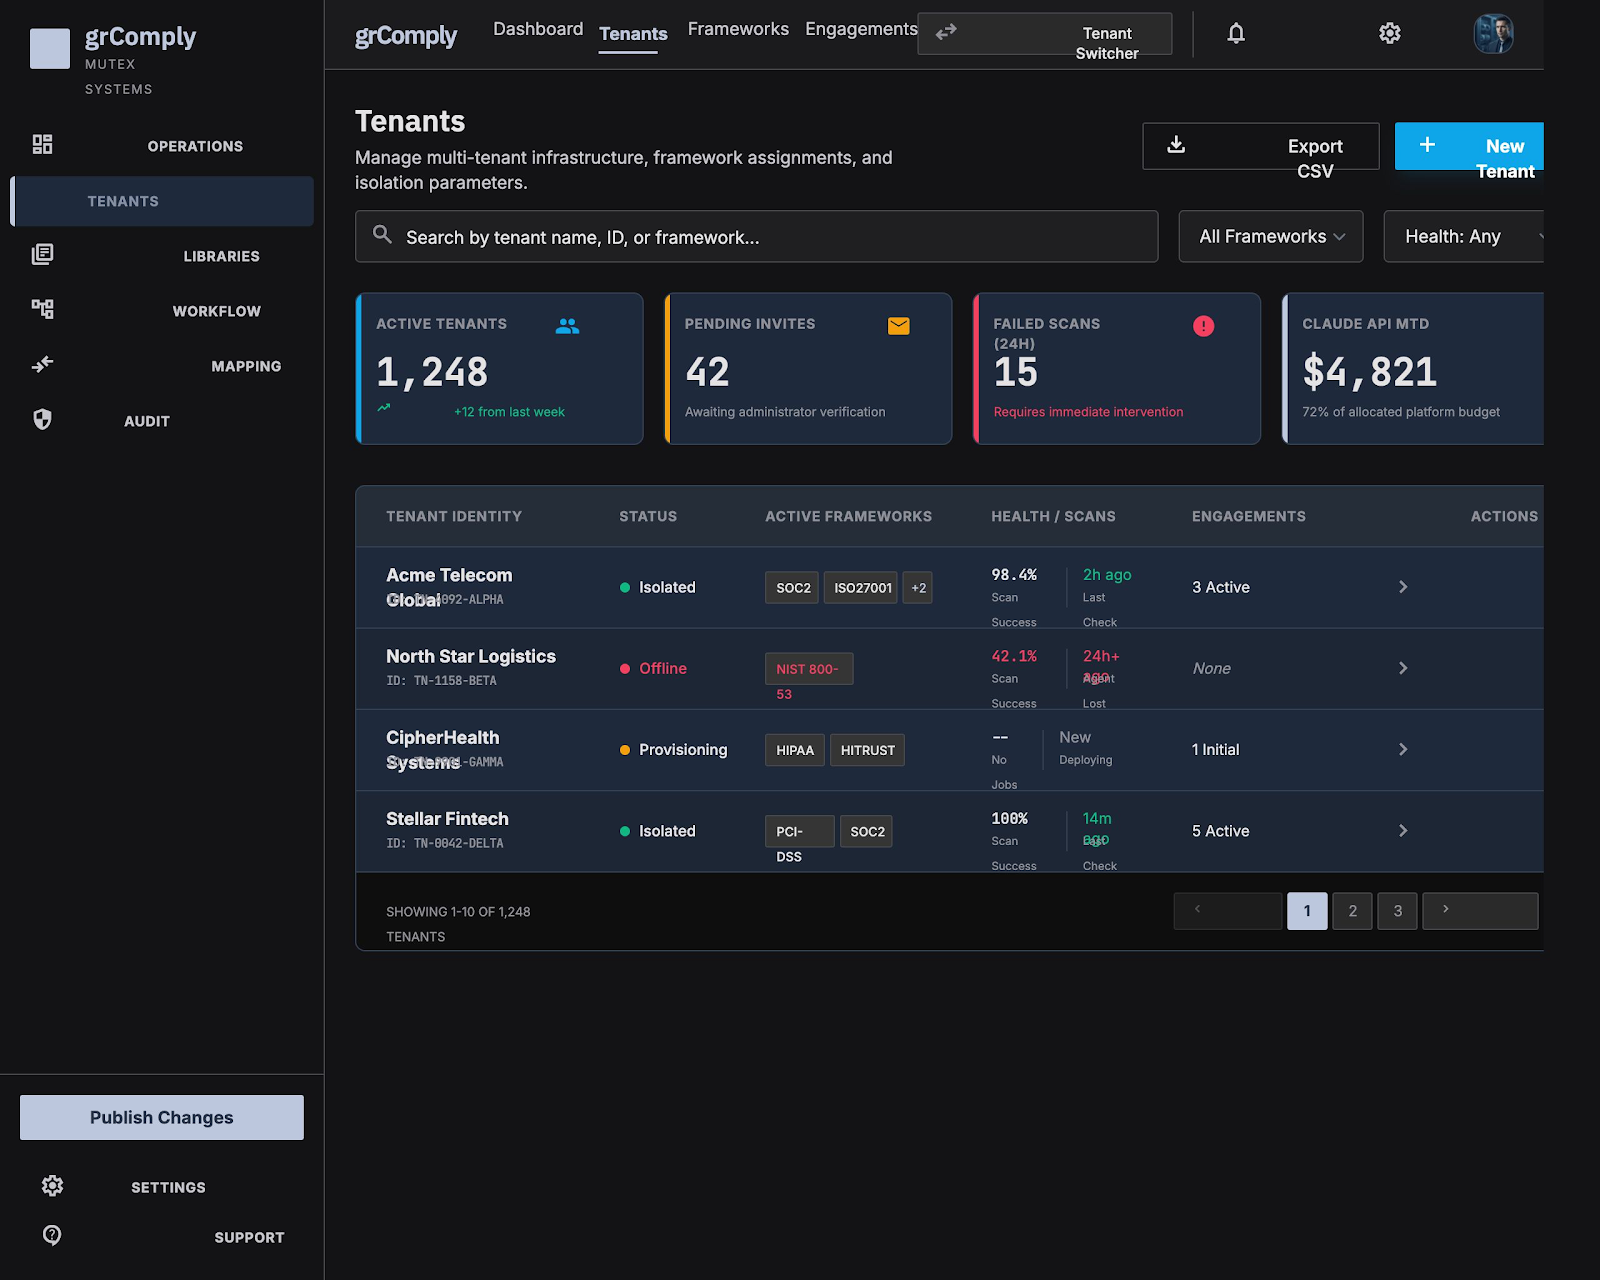
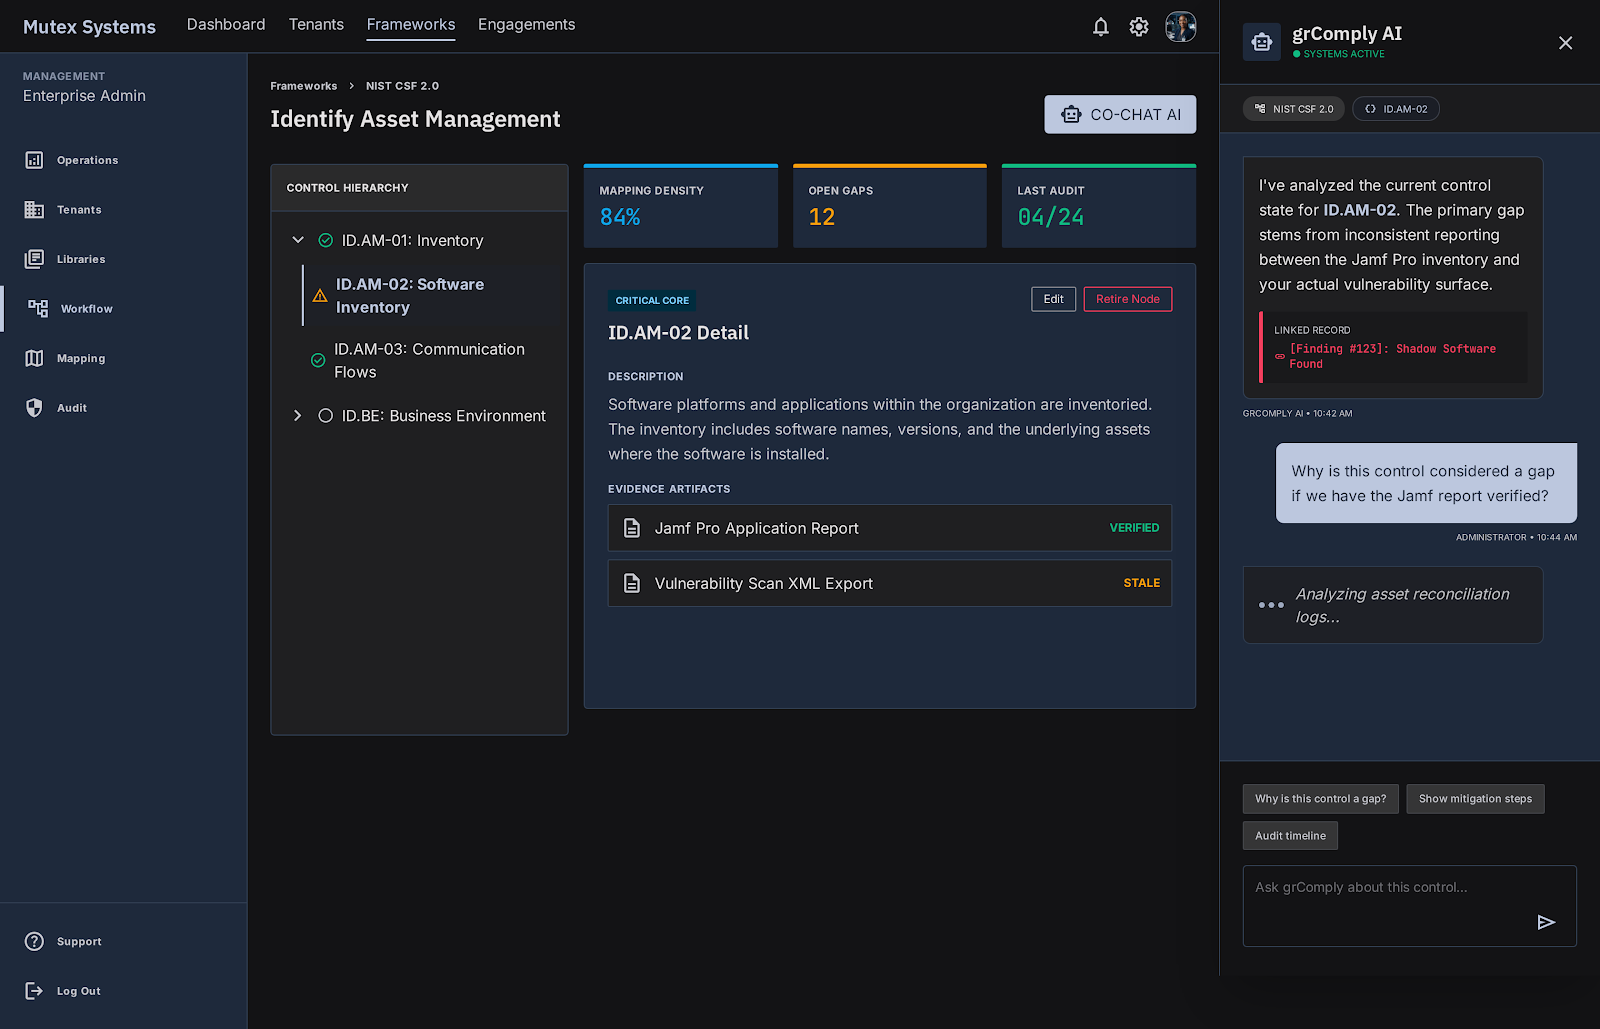
SOC 2 Type II in grComply
What is SOC 2 Type II?
SOC 2 Type II is an AICPA attestation that tests whether an organisation's controls were both suitably designed and operated effectively across a defined examination period, typically 3 to 12 months — more rigorous than Type I's point-in-time design check.
Does grComply support the full SOC 2 Type II structure?
Yes — the identical comprehensive TSC 2017 seed used for Type I: 5 series, 20 Criteria, 61 Points of focus — tracked with dated, period-spanning evidence rather than a single as-of snapshot.
How long does a Type II examination period need to be?
Typically 3 to 12 months, set by your auditor and business needs; grComply's scheduling and dated evidence trail work the same regardless of the period length you choose.
What happens if a control fails partway through the period?
It's tracked as a gap with remediation evidence attached and dated, giving your auditor an honest, traceable exception record rather than a control that quietly disappears from a year-end summary.
Can we go straight to Type II without a Type I first?
Yes, though many organisations run Type I first to prove design before committing to a longer Type II examination window — grComply supports either path on the same seeded control tree.
Does continuous scanning help with Type II specifically?
Yes — scheduled external and internal scanning produces dated, CVE-enriched findings throughout the examination period, which is exactly the kind of continuous evidence a Type II sample-testing approach is designed to sample from.
Can SOC 2 Type II evidence also satisfy other frameworks for the same period?
Where controls are genuinely equivalent, yes — cross-framework mapping lets dated evidence credit an equivalent NIST CSF or ISO 27001 control for the same date range, not just SOC 2 alone.
How is the final report different from Type I's?
It documents operating effectiveness across the whole period, including any noted exceptions and remediation, versioned and traceable back to source evidence. See SOC 2 Type I for the point-in-time version.
See SOC 2 Type II mapped into your control library
Powered by Mutex Systems. Back to Compliance Frameworks → · grComply overview → · Security Awareness Training →
Talk to us about SOC 2 Type II
Tell us where your SOC 2 Type II programme stands today, and we'll route it to the right product specialist.
- A product specialist replies personally — not a bot
- No obligation after the first conversation
- WhatsApp support also available 24/7
By submitting, you agree to be contacted about your enquiry. We respect your privacy.
Book a meeting directly
Pick a time that works for you — 30 minutes with a product specialist, no sales script.
Ready to bring SOC 2 Type II into one control library?
We respond within one working day — or reach us instantly on WhatsApp.